Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Discovering and Blocking a Zero-Day Exploit with CrowdStrike Falcon Complete: The Case of CVE-2023-36874

CrowdStrike Counter Adversary Operations is committed to analyzing active exploitation campaigns and detecting and blocking zero-days to protect our customers. In July 2023, the CrowdStrike Falcon® Complete managed detection and response (MDR) team discovered an unknown exploit kit leveraging a still-unknown vulnerability affecting the Windows Error Reporting (WER) component.
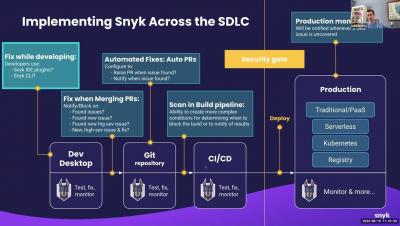
Starting Strategies: Where to Begin After Purchasing Snyk

Luke Sanders, Senior Technical Success Manager, shares quick tips and best practices for getting started with Snyk. Topics covered include: Snyk helps software-driven businesses develop fast and stay secure. Continuously find and fix vulnerabilities for npm, Maven, NuGet, RubyGems, PyPI and more.

CodeSecDays conference and more complete security coverage with GitGuardian

As secrets have a role in most security incidents, Snyk is excited to partner with GitGuardian to help development and security teams scale their security programs and further reduce an application's attack surface at every stage of the code-to-cloud lifecycle. We recently spoke at GitGuardian's first digital conference, CodeSecDays, joining security leaders from Chainguard, Doppler, Kondukto, and more — who shared insights on software signing, open source security, and secrets management.

The Impending EOL of CentOS 7: What You Need to Know and How to Prepare

CentOS 7 has been a popular choice for many businesses and developers due to its stability, robustness, and compatibility with enterprise-level applications. According to W3Techs, CentOS is used by 2.8% of all the websites whose operating system is known. However, as announced on the official CentOS blog, the end of life (EOL) for CentOS 7 is fast approaching. This means that after June 30, 2024, CentOS 7 will no longer receive official support, updates, or security patches.

BitForge: Fireblocks researchers uncover vulnerabilities in over 15 major wallet providers

The Fireblocks cryptography research team has uncovered BitForge – a series of zero-day vulnerabilities in some of the most widely adopted implementations of multi-party computation (MPC) protocols, including GG-18, GG-20, and Lindell17.

Defender Pretender: When Windows Defender Updates Become a Security Risk

The SafeBreach Labs team is committed to conducting original research to uncover new threats and ensure our Hacker’s Playbook provides the most comprehensive collection of attacks. As part of our recent research efforts, we discovered a vulnerability in the Windows Defender update process that could effectively allow an unprivileged user to take full control of the Windows Defender tool and leverage it for future malicious activities.

IoT Monitoring: Protecting & Maintaining IoT Devices in 2023

The state of cybersecurity is in constant flux — meaning we must constantly iterate and revisit our systems to protect ourselves. With security logging and monitoring failures moving up to number 9 of the OWASP Top 10, organizations everywhere are revisiting their stance on network and application monitoring. This is great for getting a pulse check on security posture and is certainly key in any good strategy, but we might be forgetting something — IoT devices.