Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How multi-agent systems work in LimaCharlie

This video walks through how single agents and multi-agent systems are built and run inside the LimaCharlie platform. Agents in LimaCharlie are defined declaratively. Each agent specifies the model it runs, its instructions, the tools it can access, what events trigger it, and the guardrails it operates under. This approach makes agents version controllable, reviewable, and portable across tenants.
Are we blindly giving AI access to everything?

Users are connecting AI tools without understanding the security implications. In this week's Intel Chat, Chris Luft and Matt Bromiley discuss a security breach at Vercel that originated from a compromised third-party AI tool used by one of its employees. The attacker gained control of the employee's Google Workspace account, which provided access to Vercel's internal environment.

AI SecOps Worskhop Series: Detection Engineering with LimaCharlie and Claude Code

This hands-on workshop is designed for security professionals interested in learning how to integrate advanced AI capabilities into their detection and response workflows. Attendees will receive practical, step-by-step instruction on leveraging the power of Claude Code, a sophisticated AI agent, to significantly enhance security operations within the LimaCharlie platform for detection engineering use cases.

The Adversary's Speed Just Changed - What Mythos Means for Your Security Posture

The cybersecurity threat landscape just changed — and most organizations don't know it yet. In this conversation, Tanium's Pedro (CRO) and Mark Liu (VP of Solution Engineering) break down what Anthropic's Mythos really is, why security leaders everywhere are asking about it, and what organizations need to do right now. No marketing pitch — just a straight conversation about a consequential shift that's already underway.

CrowdStrike Expands ChatGPT Enterprise Integration with Enhanced Audit Logging and Activity Monitoring

As organizations scale ChatGPT Enterprise across departments, AI is becoming embedded in everyday business operations. Finance teams are building custom GPTs. Developers are leveraging Codex to act on codebases. Employees are invoking third-party tools within AI conversations to automate workflows. As adoption accelerates, security teams face a fundamental challenge: visibility around agents deployed and running in SaaS environments.

How a Hacker Used Standard AI to Dismantle a Government

The real shock is not a restricted model with scary branding, it is what standard public AI tools already make possible. A prolonged attack against government systems, tax records and voter data shows the threat comes from scale and persistence, not only from the newest frontier release.

Continuous Threat Exposure Management (CTEM): The Complete Guide to Proactive Cybersecurity

The cybersecurity landscape has fundamentally changed. Organizations today manage sprawling digital environments - cloud workloads, remote endpoints, SaaS applications, third-party APIs, and hybrid infrastructure - all of which expand the attack surface at a pace that traditional security programs simply cannot match.

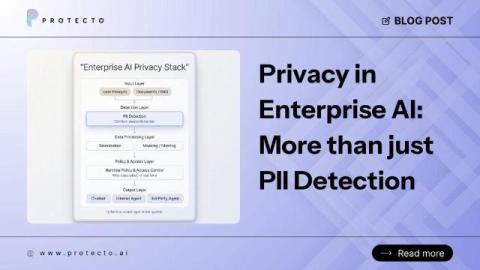
Privacy in Enterprise AI: Why It's the Foundation, Not a Feature

Last week, OpenAI released Privacy Filter, an open-weight model for detecting and redacting PII in text. It is a thoughtful release: Apache 2.0 licensed, able to run locally, designed for high-throughput workflows, and built to go beyond regex-based detection. This is good news for everyone building enterprise AI. Privacy at the model layer is getting real attention. What we liked most was how clearly OpenAI described the role of the model.

How Do AI Agents Create Data Exfiltration Risk?

AI agents create data exfiltration risk by combining three capabilities that are dangerous together: access to private data, exposure to untrusted content, and the ability to communicate externally. When all three exist in one agent, an attacker can hide instructions inside an email, document, or webpage the agent processes and trick it into sending sensitive data out. No software vulnerability is required. The attacker doesn't need to break in. They just need to talk to your agent.