Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Introducing your AI interaction layer

AI is everywhere, but without a consistent and secure way to connect it to real systems, it remains fragmented, difficult to govern, and hard to scale. Today, we’re introducing your AI interaction layer. Tines unifies AI agents, copilots, and Model Context Protocol (MCP) servers and clients in a single, secure environment. It gives teams a practical way to connect AI to systems and put it to work seamlessly across operations.
LLM Security Checklist: Essential Steps for Identifying and Blocking Jailbreak Attempts

If your organization uses a private large language model (LLM), then it’s time to start thinking about countermeasures for jailbreaking. A jailbroken LLM can lead to leaked information, compromised devices, or even a large-scale data breach. Even more troubling: Jailbreaking LLMs is often as simple as feeding them a series of clever prompts. If your customers can access your LLM, your potential risk is even higher.

Token Torching: How I'd burn your AI budget (so you can fix it)

I spend most of my time thinking like a criminal. Not because I’m edgy, but because that’s literally the job. And lately, everywhere I look, I see the same thing: People are exposing MCP endpoints like they’re REST APIs, and forgetting they’re actually money execution engines. So let’s talk about Token Torching. Yes, I invented another name. This isn’t data theft. It’s not taking your service down.

7 Smart Ways to Improve Security Monitoring With Automation

Security can feel like a constant background concern for anyone who runs a startup or manages product delivery. One missed alert or late response can cause serious damage. Manual monitoring is no longer effective, as it doesn't scale well. Workers get tired, which causes logs to pile up and signals to be easily missed. That is why many businesses are turning to automation.

New Cloudflare report warns of a 'Technical Glass Ceiling' stifling AI growth and weakening cybersecurity

New research shows that organisations modernising apps are 3x more likely to see AI payoffs, while those clinging to legacy systems face rising security risks and developer talent shortages.

ServiceNow's Virtual Agent Vulnerability Shows Why AI Security Needs Traditional AppSec Foundations

The recent disclosure of what security researchers are calling "the most severe AI-driven vulnerability uncovered to date" in ServiceNow's platform serves as a stark reminder: securing agentic AI isn't just about new AI-specific controls; it requires getting the fundamentals right first.

Arctic Wolf and AWS: AI-Powered SOC and Security Incident Response

Discover how Arctic Wolf partners with Amazon Web Services (AWS) to deliver cutting-edge, AI-powered Security Operations Center (SOC) capabilities and advanced security incident response solutions. This video explores how Arctic Wolf leverages AWS cloud infrastructure and artificial intelligence to provide: Learn how this powerful combination enhances your organization's security posture, reduces response times, and protects against evolving cyber threats through intelligent automation and comprehensive managed detection and response (MDR) services.

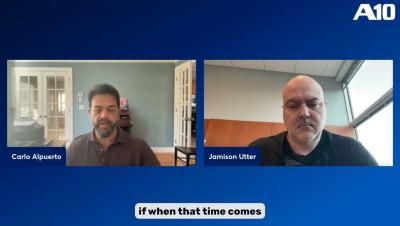
How Agentic AI Creates Shadow APIs: Security Risks Explained

How Agentic AI Creates Shadow APIs: Security Risks Explained As businesses move from static applications to Agentic AI, the security landscape is shifting beneath our feet. In this clip from the A10 Networks webinar, "APIs are the Language of AI: Protecting Them is Critical," experts Jamison Utter and Carlo Alpuerto discuss a new frontier in cybersecurity: AI that builds its own APIs.