Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

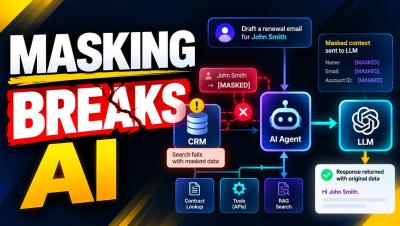
Why Data Masking Breaks AI Workflows (And What Works Instead)

What if masking sensitive data actually broke your AI application? Most AI security strategies start with a simple rule: mask sensitive information before it reaches the LLM. But real AI workflows are more complex. An AI agent might need to search a CRM, retrieve a contract, check account details, call external tools, and generate a response. Each step may require a different level of access to sensitive data.
Agentic AI and PCI DSS: What Happens When AI Agents Reach Checkout?

An AI shopping assistant can recommend a product without being allowed to buy it. An agentic AI system may go further: access an account, select a payment method, interact with a checkout, and initiate a transaction. Each added permission changes the payment-security questions you need to answer. Before adding an agent to a payment journey, draw its boundary. What can it read? What can it change? What can it authorize? What happens when it encounters content controlled by someone else?

Introducing Sophos AI Defense

Sophos AI Defense finds the AI tools employees and applications are using, including the ones security teams never approved, and enforces policy wherever they run. Every AI tool an organization can’t see is a potential gap in confidentiality, integrity, and availability. Delivered through Sophos Fusion, the AI-native cybersecurity defense system, Sophos AI Defense connects controls on the device, across the network, at sign-in, and in the browser into one line of defense, so teams can safely adopt AI faster without adding another disconnected tool to manage.

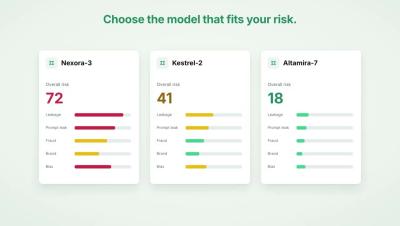
Cato AI Red Teaming: Find AI Model Risks Before Attackers Do

AI-powered applications depend on the models behind them, and those models keep changing. New attack techniques appear every day, model updates can change how safeguards behave, and switching models can leave existing protections behind. Security teams need to know where their AI is exposed before an attacker finds out first.

Three AI SOC Differentiators That Separate Real From Marketing

Every vendor in this category now says the same word: agentic. I understand why. It’s what the market wants to hear. But when you’re the one signing the contract, “agentic” tells you almost nothing. I’ve sat on the buying side of enough of these conversations to know that the label and the capability are often two very different things.

Why AI Red Teaming Belongs at the Core of Your AI Security Program

Enterprises are putting AI applications and agents to work on sensitive data and business workflows, while attackers look for new ways to manipulate the models and exploit the tools connected to them. Security leaders need to know whether those systems will hold up against a real attack, and AI red teaming gives them that answer by testing AI the way an attacker would.

AI Trust Starts With Knowing the Source

An AI agent produces a recommendation that looks reasonable. It's accurate. The model didn't hallucinate. Can the organization trust it? That depends on questions the output can't answer: Enterprise trust requires knowing where information came from, how it moved, what happened to it, and whether the process behind the result deserves confidence. Provenance is where that trust starts.

MCP Gateway Security Controls for AI Agents

The Model Context Protocol states plainly that it cannot enforce these security principles at the protocol level, and that implementors should follow best practices in their integrations. Every control an organization gets therefore comes from where it places the gateway and what it does there. ‍ The protocol publishes its own security best practices document, currently at revision 2026-07-28, naming the attacks a deployment has to handle.