Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Mapping AI Interaction Monitoring to the OWASP Top 10 for LLMs

Interaction monitoring covers four of the ten risks in the 2025 Top 10 for LLMs and generative AI applications well, three partially and three not at all. The split is not arbitrary, and the line it follows tells a buyer more than the coverage count does. ‍ Monitoring observes systems being used. Several entries on the list describe defects in how a system was built, which no amount of observation at the point of use will surface.
Governing AI Coding Agents on Developer Laptops

A coding agent on a laptop runs as the developer. It reads the same keychain, carries the same tokens and appears in every downstream log under the same name. The identity record is accurate and it cannot answer the question governance needs answered. ‍ Every control keyed to identity therefore operates on a merged subject.

Detection engineering meets AI-driven adversary emulation

In the first post in this series, Wade shared how our team laid the foundation for using AI in detection engineering. The short version is that an LLM doesn't know your stack. Without documentation and workflow context, it can produce plausible results that are difficult to trust, regardless of which model you use.

AI found the flaws. You don't need 1,000 contractors to fix them.

On October 14, 2026, Bank of America's CEO said the bank brought in 1,000 contractors to patch software flaws surfaced by frontier AI models, including Anthropic's Mythos. "We put on 1,000 contractors to help us do the patching work in the second quarter," Brian Moynihan told CNBC. Those contractors work on top of the 3,000 people the bank already has in that area (ITPro, The Next Web). That is what the new normal looks like.

Generative AI security risks every enterprise should prepare for

Over time, we have become increasingly accustomed to using AI in our daily work. We send customer data to ChatGPT for analysis, share customer emails to draft responses, or ask Claude to generate code for enterprise applications. All of this can happen within an enterprise environment. This is what generative AI is designed to do. It creates content for us, from text and code to images and videos.

Demo-grade AI vs enterprise-grade AI in GRC tools: What's the difference?

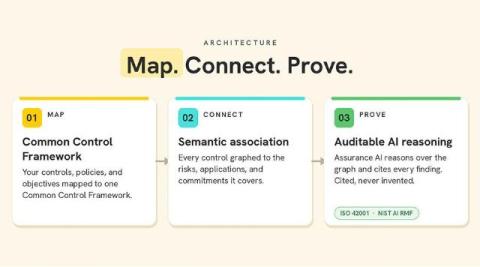
Most GRC platforms claim to use AI. That makes it harder, not easier, to judge the near-identical claims in every demo. Leaders need to know the standards to hold these claims to, what can actually be verified, and how to tell two product pitches apart before letting one of them touch critical controls. It helps to split what you are looking at into two groups: demo-grade AI and enterprise-grade AI. Nearly every GRC vendor now describes itself as the second.

Warning: Phishing Attacks Are Using AI-Themed Ad Lures

A phishing campaign is using AI-themed lures to target employees who operate advertising accounts, according to a new report from Island. The campaign is launched from a phishing platform that poses as a portfolio of AI advertising tools, using branding from Gemini, Claude, ChatGPT, Perplexity, and Muse. The platform’s operator added a fake Muse Ads lure eight days after Meta launched its Muse AI agent.

How AI Audit Trail Confidence Grows With Each Connected Source

An audit trail is usually judged by how much it contains. The more useful question is how many innocent explanations it rules out, because a record that admits a benign reading supports an assertion rather than a conclusion. ‍ Each source added to a trail removes an alternative explanation rather than adding detail. Confidence therefore climbs in steps rather than smoothly, and three sources of the same kind are worth less than two of different kinds. ‍

The Best AI Governance Platforms for Mid-Market Companies

Enterprise AI governance guidance assumes a review board that meets monthly, an independent validation function, an impact assessment per system and somebody whose job title contains the words AI and compliance. A company of three hundred people has none of those and is governed by the same regulations. ‍ The difference runs deeper than budget. Enterprise programs are assessment-led, which scales with headcount because every system needs an assessor.

What Is Reach Security? Autonomous Defense for the Security Controls You Already Own

Reach brings autonomous defense to the security controls organizations already own. AI-powered attackers can find and exploit misconfigured controls, configuration drift, and unpatched vulnerabilities in minutes. Reach helps defenders find and close those gaps first. It mitigates vulnerabilities with compensating controls, autonomously finds and fixes misconfigured security controls, and stops configuration drift.