Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

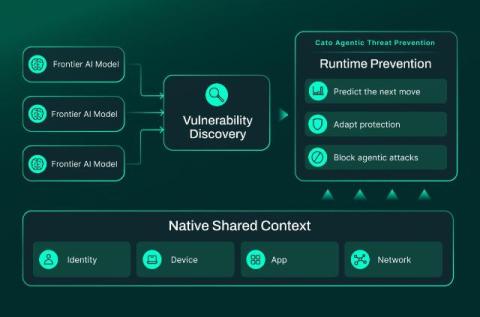
Beyond Model Access: Frontier AI Defense Needs Runtime Prevention

Access to powerful AI models is opening new possibilities for cybersecurity. Models can help uncover weaknesses, investigate threats, and explore how attackers might break into an environment. Using several models can bring different strengths to that work. But model access alone does not answer a critical question: can your defense stop an attack while it is happening? In the frontier AI era, discovery needs to connect to action.

Your AI Transformation Needs Runtime Protection for the Whole Agentic Estate

AI Detection and Response (AI-DR), also called AI runtime security, is quickly becoming a must-have. Prompt injection, jailbreaks, and data leakage are real, and the prompt is often where attacks begin. But the prompt is only the first hop. In an agentic enterprise, a single instruction can trigger activity well beyond the LLM, all the way to your business systems and data.

Meet Dai Fujimoto: Building Zenity's Next Chapter in Japan

Japan’s Ministry of Finance reports that AI adoption in large local enterprises has surged to 89%. Companies are progressively choosing to incorporate AI agents into their workflows, building with Microsoft Copilot Studio, ChatGPT Enterprise, Claude, and a myriad of other platforms, all living across a variety of environments with autonomy, privilege, and minimal supervision.

Zenity for Claude Tag: Securing the Shared Agent in Your Slack Workspace

Your team just hired someone who never sleeps, reads everything, and takes work from whoever asks. That’s the elevator pitch for Claude Tag, and on the face of it, it’s hard to see why anyone would push back on the new hire. Enterprises will want this in every workspace. On-demand status updates, first drafts, streamlined triage; the work that quietly eats a week now collapses into the team conversation.

CrowdStrike and Anthropic Give Critical Infrastructure Defenders the AI Advantage

Critical infrastructure is where cyber risk becomes real-world risk. The environments powering energy, water, manufacturing, and transportation are among the most complex to defend as they often combine decades-old operational technology (OT) with modern IT. Downtime is not an option, and patching isn’t always possible. Now, AI is raising the stakes. Adversaries are using AI to move faster and operate at greater scale, compressing the time defenders have to respond to attacks.

Autonomous Pentesting: AI Agents That Test Your App 24/7

Most companies pentest their app once a year. Hackers look for new backdoors every single day. Astra Autonomous Pentesting closes that gap with AI security agents that test your web app continuously, 24/7. Traditional penetration testing gives you a giant report full of jargon that sits on a shelf. Astra works like a friendly hacker that never sleeps. When it finds a security weakness, it doesn't just send a scary alert. It explains the exact problem, with the attack story and proof, so clearly that AI coding tools can fix, test and repair the vulnerability the same day.

Agent 365: How to Find the Shadow AI Agents in Your Tenant

Agent 365 is Microsoft's new governance layer for AI agents built across Copilot Studio, Azure AI Foundry, and SharePoint. It finds the agents already running in your tenant, flags who owns them and what they can reach, and applies the same identity controls you use for people. Most organizations have more agents out there than they think.

Frontier models found the vulnerabilities. Only the attacker found the chains.

Attackers don't read your repository; they hit your URL, and chain together whatever they find. In an era where offensive AI runs against live applications at machine speed, your security tooling needs to go beyond finding vulnerabilities to prove exploitability, including whether they can be combined into a breach.

Context-Aware DLP: Why It's Vital for AI Security

Security teams can spend years tuning DLP rules for the tools they know about. But, then an employee will paste a customer list into an AI assistant that did not exist on any policy six months ago, and the rule never fires. The tool was not on the list, and once the data returns as a summary, it no longer matches the pattern a rule was written for either, creating risk the security team is completely blind to. A bigger rule set does not close this new risk gap.