Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What is the Most Frustrating Experience in SOC 2 Audit and Attestation?

The SOC 2 (Service Organization Control 2) audit and attestation process is something that has been devised by the American Institute of Certified Public Accountants (AICPA) in order to ensure that organizations which provide services have secure procedures to govern data so as not to compromise the welfare of their clients. For this reason, achieving SOC 2 compliance is crucial for service agencies especially those involved with sensitive customer data.

Cybersecurity: The Unsung Hero of SOX Compliance

The Sarbanes-Oxley Act of 2002 (SOX) was enacted to restore public confidence in the wake of major corporate and accounting scandals. The legislation aims to protect investors by improving the accuracy and reliability of corporate disclosures made pursuant to the securities laws. One key aspect of SOX compliance is ensuring the integrity and security of financial data. In the digital age, cybersecurity practices play a crucial role in adhering to SOX requirements.

The Role of Automation in Managed File Transfer: Streamlining Workflows

In an era where efficiency and security are paramount, automation has become a critical component of Managed File Transfer (MFT) solutions. Automation in MFT streamlines workflows, reduces manual intervention, and ensures that file transfers are executed consistently and securely. This article delves into the role of automation in MFT and how it contributes to streamlined business operations.

CMMC Compliance: Customer and Shared Responsibility Matrix

CMMC is a familiar framework to any contractor working as part of the defense industrial base and handling any form of controlled unclassified information. Whether it’s compliance in general, a specific clause relating to DFARS 252.204-7012 in your contract, or impetus from another source, you’re going to need to implement security standards from NIST SP 800-171 and adhere to the rules laid out in the Cybersecurity Maturity Model Certification framework.

NIS 2 and EU Cybersecurity Act: Mandatory System Hardening

The NIS2 Directive is the European Union’s flagship cybersecurity law, poised to significantly strengthen cyber defenses across the EU when it takes effect on 17 October 2024. This upgraded version of the 2016 NIS Directive (NIS1) not only introduces stricter rules but also broadens its reach, covering more sectors and businesses, ensuring comprehensive protection and a stronger security posture.

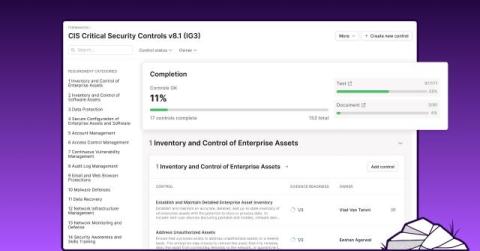
Introducing new Vanta capabilities to automatically improve your security posture

From day one, Vanta has helped security teams build and maintain a strong security posture to protect sensitive data and reduce business risk. Our industry-leading trust management platform provides automated, continuous compliance, ensuring that the necessary people, processes, and technology for strong security are in place and working effectively. ‍ With Vanta, customers like Unleash and Pigment are able to reduce costs and free up resources for strategic security initiatives.

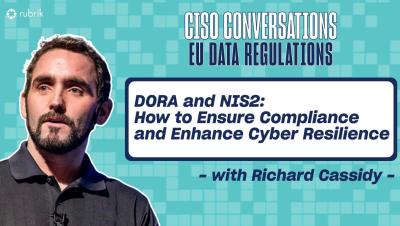
DORA and NIS2: How to Ensure Compliance and Enhance Cyber Resilience

In this episode of CISO Conversations: EU Data Regulations, Richard Cassidy, EMEA Field CISO at Rubrik is joined by Jack Poller to discuss the key differences between DORA and NIS2, how they can help enhance resilience against cyber threat, and what steps organizations need to take to ensure compliance.

4 takeaways from A-LIGN's 2024 Compliance Benchmark Report

A compliance audit shows your customers exactly what measures you have in place to keep their data and assets safe. Given that trust is such a crucial aspect of customer relationships, the quality and efficiency of your compliance audit is more important than ever. ‍ A-LIGN, one of Vanta’s technology-enabled security and compliance partners, recently released its 2024 Compliance Benchmark Report, based on an annual survey of nearly 700 business leaders and compliance professionals.