Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Enhance NIS2 Compliance: Elevate Your Cybersecurity with Awareness & Culture Before The Deadline

The NIS2 Directive, also known as the Network and Information Security Directive, is a crucial piece of legislation designed to enhance cybersecurity and protect critical infrastructure across the European Union (EU). Building on the previous NIS Directive, it addresses its shortcomings and expands its scope to improve security requirements, reporting obligations, and crisis management capabilities.
SOC 2 certification: 5 things we learned

Maybe you’re considering AICPA SOC 2 certification? Aikido was recently examined to check that our system and the design of our security controls meet the AICPA’s SOC 2 requirements. Because we learned a lot about SOC 2 standards during our audit, we wanted to share some of the insights that we think might be helpful to someone starting the same process. Read our top tips on becoming ISO 27001:2022 compliant.

Solving for CMMC: An Accelerated, Low-Risk Compliance Approach

In a recent webinar, NeoSystems and Deltek unveiled a strategy to help government contractors, compliance officers, and IT professionals achieve Cybersecurity Maturity Model Certification (CMMC) swiftly and with minimal risk. Here’s a synthesis of the critical points discussed, offering valuable guidance on how to navigate the complexities of CMMC.

Strengthening compliance and risk management with Elastic Observability: A case for India's banking sector

In navigating the complex landscape of regulatory compliance and risk management, India's banking sector faces unique challenges, particularly in meeting directives outlined by the Reserve Bank of India (RBI) and the Indian Computer Emergency Response Team (CERT-In). As organizations strive to adhere to these stringent requirements, Elastic Observability emerges as a powerful ally, offering advanced log analytics capabilities tailored to address regulatory mandates and mitigate operational risks.

How to Create a GDPR-Compliant Password Policy?

If your company has ever worked with businesses in European Union countries, you probably had to follow the EU’s General Data Protection Regulation (GDPR). This rule, which started on May 25, 2018, gives customers more control over their data and makes data collection and use more transparent. A big part of the GDPR is protecting people’s privacy and data from unauthorized access. To do this, companies need a strong password policy.

The Ultimate Guide to FedRAMP Marketplace Designations

Whenever a government agency, contractor, or subcontractor wants to work with a cloud service provider, they have to find one that upholds the level of cybersecurity, physical security, and authentication that the government sets as standard. Usually, agencies have two options to do this. They can work with a cloud service provider that is FedRAMP authorized, or they can work with one that is FedRAMP Equivalent.

Protecto - Secure and HIPAA Compliant Gen AI for Healthcare

Generative AI is often seen as high risk in healthcare due to the critical importance of patient safety and data privacy. Protecto enables your journey with HIPAA-compliant and secure generative AI solutions, ensuring the highest standards of accuracy, security, and compliance.

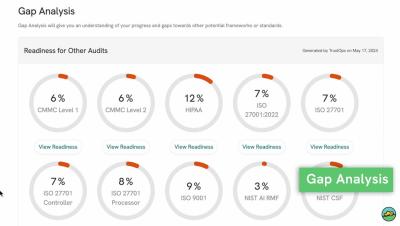
Gap Analysis - Leverage what you do now to set yourself up for success in the future as well.

How TrustCloud leverages the work you do now and sets you up for success in the future as well. Gap analysis is designed to give you insight into other compliance standards and your gaps with them. If you are looking to pursue other standards, this tool is great for determining the level of effort required from your team.

Best Cybersecurity Practices for Mac Users

Сyberattacks and the threats they pose are becoming more complex every day. Therefore, no user, including Mac users, is immune to viruses, malware, and cyberаttacks. For a long time, Mac computers were thought to be less vulnеrable to such threats than Windows ones. But that does nоt mean they do nоt need reliable protection. After all, as mentioned above, nothing stands still and threats are also improving.