Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Compliance workflow automation: making SOC 2, GDPR, and ISO auditable by design

Compliance teams know the pattern well: tracking down a missing access review sign-off at 11 p.m. the night before an audit, piecing together evidence from spreadsheets, email threads, and the gap between HR and IT. Access reviews keep appearing in SOC 2 exceptions, and the controls usually aren't the problem. The manual processes around them are. Many teams respond by buying a dedicated GRC (Governance, Risk, and Compliance) platform. Traditional GRC tools are structured repositories.
GDPR Data Security: How DLP and DSPM Support Article 32 Compliance

Article 32 of the General Data Protection Regulation (GDPR) does not specify which tools to use, however it requires organizations to implement "appropriate technical and organisational measures" to protect personal data, proportionate to the risk. What that standard’s vague wording demands in practice is where most compliance programs run into trouble.

How a Managed Security Service Provider Drives Smarter IT Solutions

For most growing businesses, trying to keep up with technology while also defending against hackers feels like a never-ending battle. Internal IT teams usually get buried under daily tech support tickets, which leaves them with no time to plan for the future or stop threats before they happen. This is where a managed security service provider (MSSP) makes a real difference. They help you move away from just reacting to problems and toward a setup that's smart, secure, and ready to grow.

Best Practices for Secure Credit Card Storage

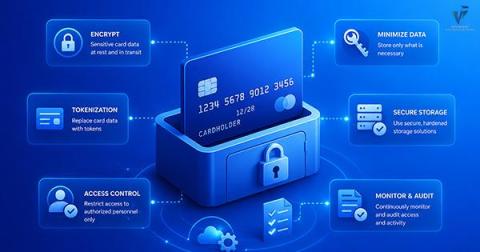
Businesses must never store CVV/CVC codes, full magnetic stripe data, or PINs under any circumstances. For PANs that must be retained, use AES-256 encryption with hardware security modules (HSMs) or, better yet, replace card data entirely with tokens via a PCI-DSS-compliant third-party vault. This removes raw card data from your environment and reduces your compliance scope from SAQ D (hundreds of controls) to SAQ A (as few as 22 controls).

Beyond the checklist: Why operational resilience is reshaping cybersecurity compliance

The days when compliance was just a documentation exercise are long gone. Now, it’s a critical priority for a wide variety of organizations. But compliance is more of a result than a goal. The goal is achieving resilience. Cybersecurity and data protection regulations are rapidly evolving far beyond traditional compliance checklists. Global frameworks and regulations such as NIS 2, DORA, GDPR, HIPAA, SOX and NIST 2.0 are placing greater emphasis on operational resilience.

The foundation of security compliance for financial services businesses

One of the less surprising findings of the 2026 Verizon Data Breach Incident Report (DBIR) is the fact that incidents targeting the Financial and Insurance sector are on the rise. As they put it, “This sector continues to be a favorite among attackers, which isn’t surprising given that its core business is handling money.”

How Research Universities Can Prepare for CMMC Level 2 Compliance

The Cybersecurity Maturity Model Certification (CMMC) is a Department of Defense (DoD) framework made to ensure organizations handling federal information maintain adequate cybersecurity controls. While CMMC is often associated with government agencies and defense contractors, research universities involved in DoD-funded projects may also need to protect Controlled Unclassified Information (CUI) like research data and technical specifications.

Building a risk taxonomy: A guide to classifying risks

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

When the actor disappears: CIS Controls in a world of non-human corporations

Every control framework makes a silent assumption. It assumes someone did it. A file changed: someone ran a script. A service account was created: someone provisioned it. A configuration drifted from baseline: someone pushed a change, applied a patch, or made a mistake. The entire architecture of CIS Controls, like most security frameworks, is built on the premise that human intent sits somewhere upstream of every action.

Best GRC Healthcare Compliance Software for Hospitals and Clinics

Most healthcare compliance teams aren't failing because they lack effort. They're failing because they're managing HIPAA, HITECH, and CMS obligations across spreadsheets, shared drives, and siloed departments that don't communicate. The best GRC healthcare compliance software solves that problem entirely. After reviewing platforms for feature depth, audit-readiness support, vendor risk tracking, and real-world reviews, the options in this guide represent what actually holds up under the pressure of a real compliance program. Here's what to expect.