Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why Doctors Recommend an Upper Endoscopy

Understanding the reasons for endoscopy can help ease the anxiety that often comes with medical procedures. For many patients, especially seniors, hearing that a doctor has recommended a diagnostic test can be concerning. However, an upper endoscopy is a routine and highly effective tool used to examine the digestive tract. It allows medical professionals to visually inspect the esophagus, stomach, and the first part of the small intestine (duodenum) to diagnose and treat various conditions.

When the Classifier Is the Judge: What the Adelphi AI Case Reveals About Automated Verification

Orion Newby was a student at Adelphi University when a single automated score nearly ended his academic career. He had written a course paper himself, working with tutors from a university support program for students with learning and neurological differences. The essay was run through an AI detector, which reported it as AI-written. On the strength of that output, Newby was accused of an integrity violation, the kind of charge that can escalate toward suspension or expulsion on a repeat offense.

WireGuard vs OpenVPN: What Actually Matters for Everyday VPN Security?

Many people look at the protocol first when choosing a VPN. WireGuard sounds newer and faster. OpenVPN sounds mature and dependable. The question quickly becomes: which one is safer? It is a useful question, but it is not complete. VPN protocols do matter. They help decide how the encrypted tunnel is created, how the connection is verified, and how data moves between your device and the VPN server. But in real use, a VPN is not trustworthy just because it supports a certain protocol.

Shadow AI has officially entered the enterprise

AI tools have become a workplace staple, but their unsanctioned use has given rise to shadow AI. It refers to the untracked usage of any AI tools or applications without approval or overview of the information technology (IT) or security team. This is substantiated by the Verizon 2026 Data Breach Investigations Report (DBIR) which shows how rapidly the shadow AI trend is growing.

Your Email is Protected. Is Your Teams Chat?

For years, security teams have poured resources into locking down the inbox, and for good reason. Email has always been the front door for phishing and social engineering. Unfortunately, another door has been left wide open: Microsoft Teams. Threat actors are increasingly posing as IT helpdesk staff inside Microsoft Teams chats, exploiting the built-in trust employees place in their internal collaboration tools to steal credentials and take over accounts.

Hyper-Targeted Social Engineering Needs Real-Time Video Response

There’s an important metric that can tell you exactly how vulnerable your high-risk employees and departments are to the next generation of social engineering. It’s not phishing click rates or training completion percentages. It probably doesn’t show up on any security dashboard. It’s the precise number of days it takes your team to respond to a live, context-specific threat with adequate training – training time to market.

What You Need to Know about the Medtronic Data Breach

Medtronic Plc is an American-Irish medical device company founded in 1949. As one of the largest medical device companies in the world and with over 90,000 employees, the company operates in about 150 countries. Its products treat 70 health conditions, helping an estimated 75 million people globally every year. Earlier in 2026, the company was the victim of a cybersecurity incident that impacted some of its corporate IT systems.

CERT-In AI Security Blueprint 2026: Remediation Timelines Every Indian Organisation Should Know

If a known exploited vulnerability appeared on your internet-facing application right now, what would your team actually do in the next 12 hours? What would actually happen, given your tooling, your sprint cycle, your change management queue, and who is available. CERT-In’s blueprint sets these timelines because generative AI and autonomous agents have collapsed the attacker timeline to the point where anything longer is already too slow.

Vulnerability Assessment: Definition, Types, Process, Cost, and Benefits

Vulnerability assessment is a systematic process that finds, assesses, and prioritises vulnerabilities in a system or application. Vulnerability assessment is considered a part of a larger family of vulnerability management. Vulnerability management is related to vulnerability analysis to identify conditions that lead to decision-relevant outcomes.

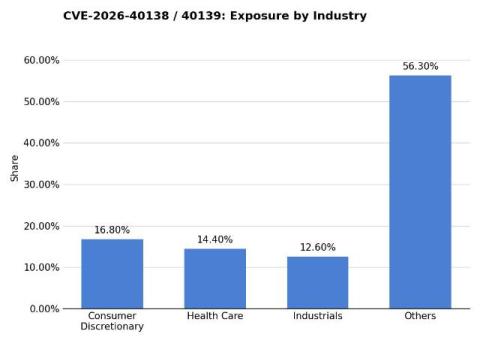
Emerging Threat: (CVE-2026-40138 & CVE-2026-40139) BeyondTrust Remote Support Authentication Bypass

CVE-2026-40138 and CVE-2026-40139 are two pre-authentication vulnerabilities in the authentication subsystem of BeyondTrust Remote Support (RS) and Privileged Remote Access (PRA), stemming from improper validation and processing of authentication data. Both carry a CVSS v3.1 base score of 9.2 (Critical).