Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How AI Is Changing Both Cyberattacks and Cyber Defense

Artificial intelligence is changing cybersecurity because it gives both attackers and defenders more speed, scale, and flexibility. Attackers can use AI to write better messages, test code, scan targets, and move through stolen data faster. Security teams can use similar technology to detect odd behavior, sort alerts, and respond before a small incident becomes a serious breach. The biggest shift is not that AI replaces every hacker or every analyst. Work that once required hours, special training, or a larger team can now be assisted by software.
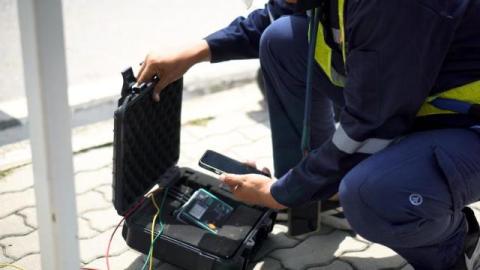
HDD Locating Frequency Selection: Why Multi-Frequency Transmitters Matter

Single-frequency locating can work on clean, shallow, predictable bores. Modern HDD sites rarely stay that simple. U.S. crews drill through utility corridors, reinforced pavement, dry soil, wet clay, rail crossings, and active electrical noise. Frequency choice now affects whether the receiver shows a stable drill position or sends the crew into guesswork.

Top 7 CDN Services That Improve Speed While Protecting Your Website

Website speed and website security used to feel like two separate projects. In 2026 they're basically the same conversation. When your pages load slowly, users bounce and ad costs creep up. When scrapers, probes, or traffic spikes hit your site, a "speed issue" turns into downtime (or at least a costly performance day).
Featured Post

The Control Paradox: Why Regulated Industries Must Rethink AI in Security Operations

For decades, highly regulated sectors have taken a cautious approach to cybersecurity, and for organisations in industries such as banking and finance, healthcare, insurance and critical national infrastructure, the instinct has been to retain ownership of security operations. That model is now under strain. Escalating cyber threats, regulatory scrutiny, and a growing skills shortage are exposing the limits of traditional Security Operations Centres (SOCs). At the same time, AI-driven technologies are maturing rapidly and forcing a strategic rethink.

What is AI Policy Enforcement and How Do You Implement It?

Here’s the reality that most security teams are already living: Over 80% of employees are using unapproved AI tools at work, and nearly half are actively hiding them from IT. The question facing every organization is no longer whether to adopt artificial intelligence — it’s how to secure the sensitive data flowing into it every single day. This is the governance gap.

Top tools for Confluence backup

Confluence is often used to store important knowledge inside an organization: runbooks, technical documentation, project plans, onboarding materials and incident notes along with internal procedures. When this data is deleted, overwritten, corrupted or simply unavailable, teams can lose the information needed to keep work processes moving forward.

Unlock Compliance Management Solutions for 2026

You can usually tell when a compliance program is still running on audit season logic. Three weeks before an assessment, Slack fills with evidence requests. Security exports screenshots from cloud consoles. IT pulls user lists from IAM. HR scrambles to prove termination workflows. Someone opens the spreadsheet nobody has touched since the last audit and starts guessing which controls still map to which systems.

Certificate lineage: the concept your tools already use but nobody named

The word “certificate” means too many different things. When someone says “the certificate for example.com,” they might mean the public key the CA signed. They might mean the key-pair sitting on the filesystem. They might mean the signature that expires in 47 days. Or they might mean all the things together, that you’ve been renewing for the last 10 years. That last one doesn’t have a name in any PKI standard. And it should.

SOC 2 Type 2 Audit Requirements for Fintech Companies

Rate this post Last Updated on June 8, 2026 by Narendra Sahoo Contents hide Why Fintech Companies Can No Longer Afford to Skip SOC 2 Type 2 What Is a SOC 2 Type 2 Report? (And Why Type 1 Is Rarely Enough) The Five AICPA Trust Services Criteria — Applied to Fintech Core SOC 2 Type 2 Audit Requirements for Fintech Companies The Practical SOC 2 Type 2 Audit Checklist for Fintech Companies Reading Your Audit Report: The Four Auditor Opinions Explained Frequently Asked Questions.