Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Introducing full transaction detection for Cloudflare WAF

Today, we are expanding our web application firewall (WAF) by adding two new capabilities: full transaction detections and response rules. Full transaction detections evaluate each HTTP request alongside its response to identify evidence of exploitation. It helps answer both "Does this request look malicious?" and "What happened when the application handled it?" Response rules can then block the origin’s response before it reaches the requester.
Building "php2shell" detections before coordinated disclosure

We recently collaborated with OpenAI, PHP, and a number of other organizations to respond to a pair of serious remote code execution vulnerabilities in PHP that are likely to impact the majority of the world's public web servers. PHP underpins a large part of the web, powering content management systems, online stores, and business applications. Its security matters to vital services that millions of people and organizations rely on daily.

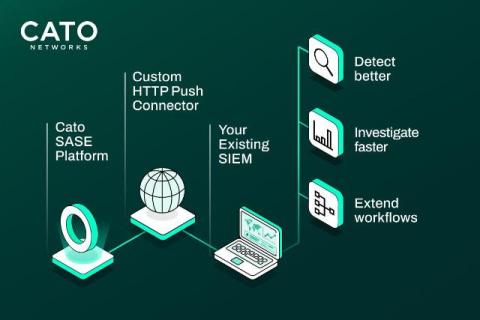
Make Your SIEM Smarter with Cato

Effective security operations require more than isolated alerts. Analysts need context from across the environment to understand what happened, assess its significance, and decide what to do next. That is why accessing insights and telemetry from across your networking and security stack is critical to teams using a SIEM tool.

Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)

On October 20, 2026, the PHP security team issued an advance security advisory regarding two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, affecting core PHP source code. Both vulnerabilities carry a critical-severity CVSS v4.0 score of 9.2 and could potentially allow unauthenticated remote code execution (RCE) on affected servers. The official patched PHP releases are now available.

CertKit now has 86 built-in deployment templates

There are lots of ways to get a certificate. Getting it onto your Cisco ISE, IBM i, or WatchGuard VPN is the hard part. We keep making that easier. Since July, CertKit has added 51 new deployment templates, more than doubling the library to 86. Each platform has a built-in deployment template, and most have a deployment guide for the setup details. Setup is just picking a certificate and setting a few variables.

AI Is Calling In Every Risk You've Accepted: Seven Insights From The AI Security Panel: Unfiltered

On October 14th, the afternoon before the AI Security Summit (AISS) flagship event in San Francisco, Snyk hosted The AI Security Panel: Unfiltered. Yahoo Finance's Deirdre Bosa moderated four people who see AI security from very different seats.

How to build a CPS 230-aligned TPRM program

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Scanning AI Assets: Catching What SCA and SAST Might Miss

Your standard application security tools are designed to protect your software pipeline by checking third-party components for known vulnerabilities (via SCA), analyzing source code for security flaws (via SAST), and scanning for accidentally exposed credentials (using secret scanners). But if a developer drops a SKILL.md file into their coding agent, installs a plugin from a marketplace, or pulls in an APM manifest, your AppSec scanners may not catch it.