Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

A Prioritized Backlog Is Still a Backlog

Vulnerability prioritization helps security teams identify what matters most, but it doesn’t actually resolve exposures. Even with better visibility, deduplication, and risk-based context, vulnerabilities remain unresolved until teams investigate, remediate, and verify the fixes. Real risk reduction isn’t about how efficiently you organize your backlog. It’s about how quickly you take action to shrink it.
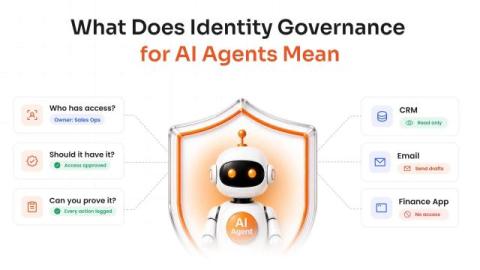
The Importance of Identity Governance for AI Agents

Identity governance answers three basic questions: Who or what has access? Should it have that access? And can you prove it later? Organizations have managed their employees this way for years. Every employee has an account, an owner, and a business reason for their access. But AI agents introduce new identities that require the same level of governance. Think about what an AI agent actually does.

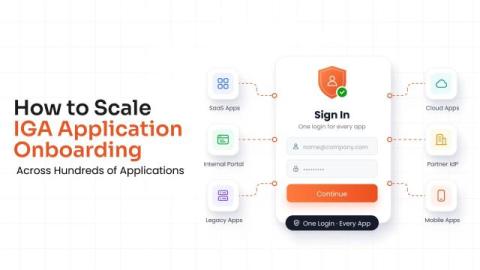
How to Scale IGA Application Onboarding Across Hundreds of Applications

An expense app, a payroll system, and a project management tool support different parts of your business. Yet each raises the same access questions: Who can use it? What are they allowed to do? And do they still need those permissions? Identity governance and administration (IGA) helps teams manage these questions. But first, each application needs to be brought into the governance process.

The Key Differences between a Sovereign Cloud vs Private Cloud

Cloud storage solutions offer different levels of control, security, and data protection, making it important to understand which option best suits your needs, whether it's for personal, business, or enterprise cloud storage. Sovereign cloud and private cloud are two popular choices, but they serve different purposes.

Q3 2026 Product Updates: What's New at Astra Security

Summer was about cutting noise. Q3 was about cutting the clicks it takes to get from “I need to test this” to “this is fixed.” This quarter, we shipped 15 updates across the Astra platform. AI agents can now run your scans through Astra MCP. Scans launch from a single screen. Schedules apply to dozens of targets at once. And when a finding lands on your desk, it comes with the proof you need to act on it. Less setup. Fewer dead-end scans. Faster triage.

Is Emergent AI Safe? Independent Pentest Findings

Is Emergent AI safe? A fair question indeed for anyone about to ship a customer-facing app from emergent.sh. Or even outside of that. Emergent is one of the fast-blooming leaders in turning plain-language prompts into full-stack web and mobile apps. What we checked is how their security holds up. Consider this a security-focused Emergent AI review. We gave four AI coding platforms the same security-explicit prompt, then attacked each app.

Vibe Coding Prompts: What Makes Them More Secure

Analyzing secure vibe coding prompts is crucial as AI adoption grows. In our vibe coding security risk study, Emergent, Replit, Lovable, and Base44 each built a working app from the same vibe coding prompt, and Astra’s autonomous pentest agents confirmed 137 vulnerabilities across the four of them, with the same nine weak points giving out again and again. If these tools build what you ask for, the obvious follow-up is what happens when you ask for something different.

AI in the SOC: Where security teams stand

With 96% of security teams now using AI, the question is no longer whether AI delivers real value to the SOC, but one of efficiency and reliability. The recent AI Adoption in the SOC report, conducted by Dimensional Research and sponsored by Elastic, surveyed more than 400 cybersecurity professionals responsible for security operations at companies with more than 500 employees.

Snyk Named a Leader in The Forrester Wave: Agentic Development Security Tools, Q4 2026

We're proud to share that Snyk has been named a Leader in The Forrester Wave: Agentic Development Security Tools, Q4 2026. Snyk received the highest score in the Strategy category, along with the highest scores possible in these criteria.

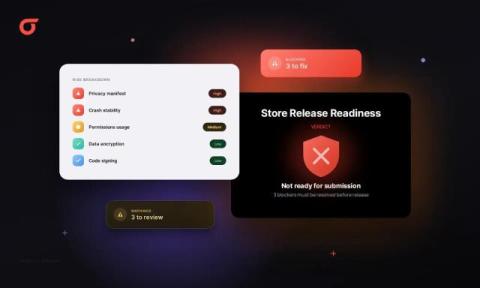
App Store Release Readiness: Know What Could Get Your App Rejected

Product launch: Appknox now checks every uploaded build against Apple App Store and Google Play submission requirements, so blockers surface while you can still fix them. Many mobile release processes have a security gate. Fewer have a store gate, so the first full check against Apple's and Google's rules often happens after the build is final and the date is public. That's the gap Appknox Store Release Readiness closes.