Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

School Event Rentals: Safety Compliance Guide for Athletic Directors

Picture a fall Friday evening: students, parents, and staff gather on the athletic field for a school carnival. As the athletic director, you're not just overseeing the scoreboard-you're responsible for ensuring every rented bounce house, obstacle course, and game booth meets safety standards. The challenge lies in balancing the festive atmosphere with strict compliance, so no one is left asking tough questions after an incident.
How Google Ads Services Are Quietly Filling Dental Appointment Books

Many dental practices do not need more website traffic. They need more booked patients. That is where Google Ads services can make a quiet but real difference. This online advertising platform puts your clinic in front of people searching right now, which is why so many practices use it to turn online interest into steady appointment demand.

Expiro Malware: File Infection, Credential Theft, and Persistent Access

Expiro (also known as Xpiro) is a modular file-infector and information-stealing malware family that has been active since around 2010 and remains a persistent threat in various regions, particularly in Asia, Eastern Europe, and Latin America. Unlike typical standalone trojans, Expiro spreads by infecting executable files on the victim system, appending its malicious code while preserving original functionality.

How Kovrr's Cyber Risk Quantification Model Works

A quantified cyber risk figure arrives as a single number, and the first thing a board member, a regulator, an auditor or an actuary wants is the route back to whatever produced it. Most vendors answer that request with documentation about method. Documentation and evidence are different things. Somebody checking a figure needs to reach the records underneath it, the way an auditor works from a financial statement into the accounts and then into individual transactions.

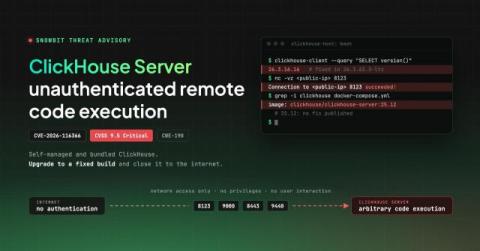
Threat Advisory - ClickHouse CVE-2026-116366: Unauthenticated Remote Code Execution

On 30 October 2026, ClickHouse disclosed CVE-2026-116366, a critical vulnerability in ClickHouse Server (CVSS v4.0 9.5). Under certain conditions, an unauthenticated attacker with network access to the server can execute arbitrary code. Third-party vulnerability trackers classify it as an integer overflow (CWE-190); ClickHouse has not confirmed this.

When Geopolitics Hits Your Balance Sheet: What Binance's $6.3B Hack Means for CTOs

Binance never chose to be on the front line of a geopolitical conflict, yet if blockchain-intelligence firms are right, that is where it ended up, and its balance sheet absorbed the first loss. Binance’s initial investigation indicates that a compromised DevOps engineer’s laptop may have given an attacker access to a service container and the ability to submit unauthorised withdrawals.

PCI Compliance Logging: Complete Guide to Requirement 10

Of the 12 Payment Card Industry Data Security Standard (PCI DSS) requirements, Requirement 10 is one your platform team can engineer directly. Under the PCI DSS v4.0.1 standard, automated log review has been a tested requirement since March 31, 2025. Your assessor will test the mechanism that performs the review. This PCI compliance logging guide covers each 10.x sub-requirement, maps the seven event classes to log sources, and lays out a nine-step program you can hand to your assessor.

Fake profile pictures: how to tell a stolen photo from an AI face

Most fake profile pictures are either a real person's photo taken without permission or a face that a generator made up. The two leave different evidence behind, so the test that exposes one will miss the other. Work out which one you might be looking at before you trust the account.

How Arrests Without a Conviction Affect Employment and Background Checks

An arrest that never leads to a conviction can still surface on a background check. Whether you can see that record-or use it-rests on strict reporting rules and anti-bias limits. On October 29, 2026, the EEOC scrapped its decade-old guidance, leaving many online explainers out of date. This guide answers four rapid-fire questions-Does the record exist? Can a vendor report it? May you weigh it? What guardrails apply?-so you keep talent moving and systems secure while staying inside the new legal lines.