Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Scanning ARM templates for misconfigurations with the Snyk CLI

Managing application resources at scale can be tricky business. As such, many DevOps and AppSec teams turn to using a declarative framework rather than writing individual scripts to deploy, manage, and maintain access controls for their resources. For Azure environments, Azure Resource Manager (ARM) is this management layer that allows teams to manage their infrastructure as code (IaC) through declarative ARM templates.
Arctic Wolf Continues on Explosive Growth Trajectory

This week marks our mid-year kick-off. It’s our all-company meeting that, like Arctic Wolf, gets bigger each year with hundreds of new team members joining us from around the world—many for the first time. With so much new hiring (we’re on pace to nearly double ourselves, again), I’m continually reminded of our Wolf Pack’s talent, dedication, and drive for success, and I’m proud to work alongside these professionals daily.

Detect & Mitigate Your Ransomware Risk with Egnyte

In this video, Egnyte’s Chief Governance Officer Jeff Sizemore & Senior Manager of Governance Marketing Neil Jones discuss recent trends in ransomware detection and how you can mitigate potential attacks. A brief demo is provided at the end, where you will learn how to recover from a ransomware attack. Ransomware attacks continue to proliferate. We want users to understand the current state of ransomware attacks and to be able to prepare for attacks and manage them more effectively.

Introduction to Custom Fields

Use custom dimensions and measures to aggregate column values or filter data. Netskope, the SASE leader, safely and quickly connects users directly to the internet, any application, and their infrastructure from any device, on or off the network. With CASB, SWG, and ZTNA built natively in a single platform, Netskope is fast everywhere, data-centric, and cloud smart, all while enabling good digital citizenship and providing a lower total-cost-of-ownership.

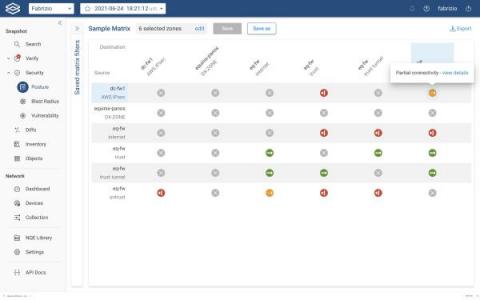
Where is Your Zone-to-Zone Connectivity Matrix?

If you’re like most of the complex IT shops we talk with, you probably don’t even have a current security matrix to store anywhere – file cabinet or data folder. The connectivity matrix is essentially the company security posture, but almost no one has a comprehensive way to visualize and easily understand the connectivity status between the various configured security policies (zone-to-zone policies).

ISO 27001 Compliance: What You Need to Know for Your Certification

Looking to become certified to the ISO 27001 standard? In this article you will learn what ISO 27001 is, the key terms and definitions, information security risks you need to consider, and the process for meeting your compliance and certification requirements.

Detecting CVE-2021-42292

On its surface, CVE-2021-42292 doesn’t look like the kind of vulnerability that a network-based tool can find reliably. Marked by Microsoft as a local file format vulnerability, security veterans would expect that between encryption and encoding, there would be a million different ways to evade network detection with a weaponized exploit.