Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Path to Autonomous Networking Starts Here

Networks have never been more critical, more complex, or more difficult to run with confidence. The infrastructure powering global finance, healthcare, and commerce has outgrown the tools built to manage it, and the teams responsible for keeping it running deserve better than guesswork. Forward is on a mission to change that.
The Forward Platform: Your Network Understood, Past, Present, and Future

Running a hybrid network today means managing complexity that the tools in your stack were never designed for. Constant change, multi-cloud environments, a security perimeter that shifts daily, and no single place to go for a verified answer about what your network is actually doing.

Forward Predict: Know the Impact of Your Network Changes Before You Push

What if your team could know exactly what a network change would do before it touched production, not a best guess, not built on incomplete data, but a mathematically verified outcome drawn from an accurate model of your actual network? That is what Forward Predict delivers.

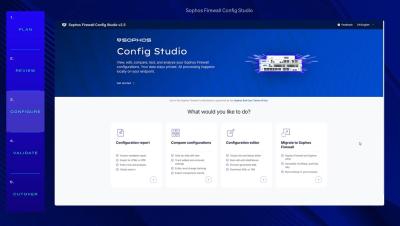
Sophos Firewall Config Studio: Migrate to Sophos Firewall

A step-by-step tutorial on using Config Studio to convert configurations from supported third-party firewalls and import them into Sophos Firewall. Learn how to review migration results, fix flagged issues, and complete the process with confidence. Ask questions and get expert answers in the Sophos Community.

Provably better data

Every security vendor says their data is better. Corelight decided to test that claim directly. Using real nation-state attack scenarios, including Salt Typhoon-related activity, the same AI model was evaluated against multiple security data sources to measure investigation accuracy, threat visibility, and incident response coverage. The only variable was the data.

RaccoonLine Technical Report Details the Efficacy of Residential P2P Nodes in Overcoming Range-Based IP Blocking

RaccoonLine, a decentralized networking provider, has released a technical report addressing the limitations of protocol obfuscation in the face of modern "range-based" IP blocking. The findings detail how national censorship systems now identify and blacklist data center IP ranges within hours of deployment, and how RaccoonLine's P2P residential node architecture provides a structural solution to this enforcement trend.

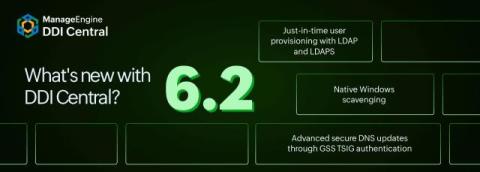
DDI Central 6.2: Now with GSS TSIG authentication, LDAP and LDAPS user provisioning, and Native Windows scavenging

DDI Central version 6.1 introduced significant enhancements to the IPAM section, bringing a segmented view for sites, clusters, and supernets, along with multiple display options: table, tree, and card views. The release also added trusted feed configurations, root hint templates, and unmapped subnet monitoring, giving network admins greater flexibility and control over their DNS and DHCP resources.