Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

WatchGuard MITRE ER7 Insights: Full Visibility, Prevention & Zero Friction

Every year, security teams and MSPs look to the MITRE ATT&CK Evaluations for one thing: clarity. Not marketing, but a transparent view of how endpoint products behave under real adversary tactics. MITRE ATT&CK Evaluations Enterprise Round 7 (MITRE ER7) is no exception. In the Windows “Hermes” scenario, modeled after Mustang Panda activity, the data shows how WatchGuard delivers strong, reliable protection with lower operational burden for security teams and MSPs.
Intel Chat: Tomiris cyber-espionage, OpenPLC ScadaBR, NPM manipulates AI scanners & MuddyWater [273]

Support our show by sharing your favorite episodes with a friend, subscribe, give us a rating or leave a comment on your podcast platform. This podcast is brought to you by LimaCharlie, maker of the SecOps Cloud Platform, infrastructure for SecOps where everything is built API first. Scale with confidence as your business grows.

WatchGuard's 2026 Cybersecurity Predictions - The 443 Podcast Episode 351

This week on the podcast, we go through all six of our cybersecurity predictions for 2026. For each prediction, we'll discuss the trends behind them, why we think they'll hit next year, and some takeaways for people and organizations on how to react to them in the coming year.

WatchGuard ThreatSync+ NDR Named Product of the Year by CRN 2025

We’re thrilled to announce that WatchGuard ThreatSync+ NDR has been named Winner Overall – Security: Network in CRN’s 2025 Products of the Year. This honor highlights not only the strength of the solution itself, but also how it aligns with, and accelerates, the major innovations shaping network security this year.

How Firebox and FireCloud Boost Security in Hybrid, Distributed Environments

A few weeks ago, a cyberattack shut down operations at the Japanese brewery Asahi, disrupting its supply chain and affecting product availability across the country. Incidents like these often take advantage of the complexity of distributed infrastructures, where insufficient segmentation between OT (Operational Technology) and IT (Information Technology) environments lets threats spread laterally uncontrolled.

Is AI taking entry-level jobs a good thing? #cybersecurity #ai #podcast

There's growing concern that AI automation is removing the hands-on experience junior analysts need to develop into senior defenders. In this Intel Chat, Matt Bromiley and Chris Luft challenge that assumption. Matt breaks down why the traditional entry-level path of endless log review and alert triage was never the best training ground to begin with. Log detection, alert triage, and drift detection are often cited as how defenders learn the trade. But most analysts never had time to get to drift detection because they were buried in repetitive work.

WatchGuard Threat Lab's top six cybersecurity predictions for 2026

WatchGuard has revealed its top six cybersecurity predictions for 2026, forecasting a year where AI-driven threats, regulatory pressures, and the decline of legacy tools will reshape the security landscape. Corey Nachreiner, chief security officer at WatchGuard Technologies, emphasises that organisations must prepare for rapid evolution in both attack methods and defensive strategies.

Is AI a cost-effective solution to alert noise? #cybersecurity #AI #SOC #podcast

Security teams are drowning in alerts, and AI might not be the answer everyone thinks it is. In this episode, Erik Bloch, VP of Security at Illumio, breaks down the math on why AI-powered alert triage may be financially unfeasible for most organizations. With 85 to 90 percent of alerts being non-malicious, security teams are still sorting through massive volumes of noise to find the real threats. Many vendors are betting that AI will solve this problem by triaging alerts at scale. But the reality?

The 9 Best Endpoint Security Solutions

Endpoint security solutions are specialized software designed to protect endpoint devices like computers, mobile phones, and tablets from cyber threats. These solutions prevent, detect, and respond to attacks by managing the security of these devices across the network. But with so many different endpoint security solutions available in the market, how can you know which is the right fit for your endpoint security strategy?

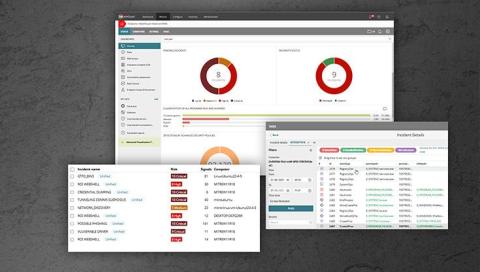
The Efficiency Shift: Protection That Scales with Your Team

Cybersecurity has a people problem. Threats scale faster than teams. Every new customer, every new endpoint, and every new alert adds pressure. Efficiency is no longer a nice-to-have; it is the only way to maintain effective and sustainable protection. That is where endpoint security efficiency comes in. Endpoint security efficiency is the ability to deliver maximum protection with minimum operational effort, turning noise into clarity and alerts into meaningful incidents.