Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Featured Post

AI Agents Are Rewriting the Rules of Identity Security

For years, identity security has been based on a fairly straightforward premise: organisations need to know who, or what, is accessing their systems, what they are authorised to do, and whether that access remains appropriate. However, the rise of autonomous AI agents has changed the game, and tore-up the traditional model of role-based access controls and privileged access management.
Kovrr's Event Catalog Brings Unmatched Transparency to the Dashboard

‍ ‍Most cyber risk quantification (CRQ) platforms ask for trust. They describe their data sources in general terms, display an average annual loss at the top of a screen, and offer nothing in between. Anybody wanting to check the number is asked to accept the connection on expert judgment alone, which is a reasonable thing to decline when the figure is about to support a nine-figure decision.

Keeper Security's Redesigned iOS Vault Features Liquid Glass and iPhone Duo Support

Keeper Security, the leading zero-trust and zero-knowledge identity security platform, today announced a major update to its iOS application with the release of version 18.1. The latest release introduces a completely redesigned vault interface utilizing Liquid Glass, support for Apple’s new dual-screen iPhone Duo and powerful automation features that simplify credential management on the go.

The Cybersecurity Community Needs to Stop Doing This

The cybersecurity community should be encouraging people to ask questions and admit what they don't know, not attacking them for it. A blunt response to the online backlash over one journalist's unfamiliarity with PHP makes the message clear: technical knowledge should never be an excuse for bullying.

Why Did a Cyber Reporter Face Backlash Over PHP and What Does It Reveal About Our Industry?

Why did the BBC's cyber correspondent face a wave of backlash for admitting he hadn't heard of PHP, and what does it say about our community? In this episode, recorded in our new Razorwire studio, I sit down with BBC Cyber Correspondent Joe Tidy, Lisa Ventura (AI and Cyber Security Association, Cyber Kindness) and Gary Hibberd (Consultants Like Us, The Real Cyber Awards) to unpack the pile-on that followed Joe's on-air admission during the PHP emergency.

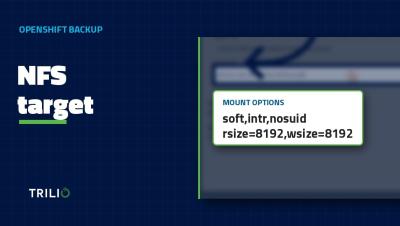
Back up OpenShift to NFS: create an NFS backup target | Trilio for Kubernetes

Create an NFS backup target for Trilio for Kubernetes on OpenShift, with the NFS mount options we recommend. You will: Best practices covered: mount with soft, not hard (with a hard mount a stalled NFS server can hang the worker node); do not tune mount options without testing a backup and a restore; Available only proves T4K can write to the export, so run one small backup and restore before you attach production backup plans.

Agentic AI Security Buyer's Guide: 6 Criteria to Evaluate

Most AI security evaluations start with the tools employees already know about: the sanctioned chatbot, the browser plugin, the approved copilot. The harder inventory of AI tooling sits on endpoints, where coding assistants, desktop agents, and custom Model Context Protocol (MCP) servers read files, query databases, and chain actions with no human approving each step.

The CIO Answers for AI They Never Approved

When an AI system misfires inside a large company, the question that follows is who was responsible for it. The answer usually lands on the CIO, and frequently the CIO had no part in choosing, approving or deploying the thing that failed. ‍ This gets described as a governance problem, which undersells it. Governance implies a process that exists and performs badly.