Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

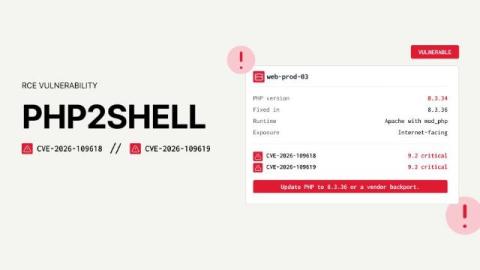
CVE-2026-109618 and CVE-2026-109619 (PHP2Shell): Two Critical PHP Remote Code Execution Flaws

The PHP security team has announced an emergency security release for Wednesday, October 21, 2026 at 14:00 UTC. It addresses two critical vulnerabilities, both rated CVSS v4.0 9.2. The vulnerabilities are tracked as CVE-2026-109618 and CVE-2026-109619. Both bugs are described as remote code execution issues, meaning an attacker could get their own commands running on a vulnerable server. The route to disclosure was messy.

Human Expertise at the Speed of AI: SentinelOne Names LevelBlue its Global Exclusive Delivery Partner for Wayfinder

Today, SentinelOne named LevelBlue its global exclusive delivery partner for Wayfinder, SentinelOne’s suite of AI-powered managed security and threat detection services. LevelBlue will deliver Wayfinder managed detection and response (MDR), threat hunting, incident readiness and response (IRR), and SentinelOne’s professional services for organizations around the world. It’s a milestone for our teams, and it reflects something we believe deeply about security in the AI era.

PHP2Shell: Responding to CVE-2026-109618 and CVE-2026-109619

If you run PHP anywhere in your environment, patch to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now. Two critical flaws disclosed this week, CVE-2026-109618 and CVE-2026-109619 (nicknamed "PHP2Shell"), let an unauthenticated attacker run code on a server with nothing more than a crafted web request. Both carry a CVSS v4.0 score of 9.2, every earlier release is affected, and exploitation in the wild has been reported. The patch is the easy part.

AI Compute Just Became an Endpoint Problem

For the last three years, enterprise AI happened somewhere else. Models trained in someone’s cloud, inference ran behind an API, and the endpoint stayed where it had always been: on a laptop that opened a browser. With local AI computing platforms like NVIDIA DGX Spark (opens in a new tab), RTX Spark (opens in a new tab), and DGX Station (opens in a new tab), that framework is ending.

CrowdStrike Uncovers New Agentic AI Campaigns

A new report from the CrowdStrike Counter Adversary Operations team details research into four previously unreported threat actors, each of whom left their offensive agent frameworks exposed via open directories. In doing so, they shared detailed insight into their use of AI agents and revealed how adversaries are quickly becoming more proficient in AI.

CrowdStrike Protects Customers from Threats Delivered via PHP2Shell

Two critical memory-corruption remote code execution (RCE) vulnerabilities, collectively dubbed PHP2Shell, have been disclosed in core PHP, the underlying engine powering a vast portion of the web. The CrowdStrike Falcon platform provides out-of-the-box visibility and detection coverage for post-exploitation activities of both vulnerabilities.

Building the Business Case for Agentic AI Security Investment

Security investment decisions are always, at some level, conversations about risk quantification: how much exposure does the organization actually carry, what does it cost to reduce that exposure, and what's the cost of not acting at all. For agentic AI security, these questions are answerable once the right measurement is in place.

Protecting sovereign AI with CloudCasa and SUSE AI Factory

A production AI service accumulates data that your team needs to recover: documents, embeddings, vector indexes, application settings, and conversation history. Once a retrieval-augmented generation (RAG) pipeline connects a model to your organization’s information, those dependencies become part of the service you operate. SUSE and CloudCasa by Catalogic are working together to protect that state in SUSE AI Factory.

The Data Center Episode: Power, Water & Local Impact | Attempted Intelligence Ep. 2

How much power and water do AI data centers actually consume—and what does their growth mean for local communities? In Episode 2 of Attempted Intelligence, hosts Harlan Parrott (VP of AI Innovation at KnowBe4) and Matt Duren (SVP of Engineering for AI & Data) go head-to-head in a friendly debate over the environmental and economic realities of AI infrastructure. A coin flip assigns their positions as they tackle the viral claims surrounding AI energy consumption, local water usage, and the trade-offs facing local governments.