Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Securing the Physical Edge: How to Plan CCTV for New York Buildings Without Creating a Network Risk

TL;DR: A CCTV system is a set of networked computers that happen to point at doors. Plan the cable path, the network segment and the recording location before you choose camera models. Then assign someone to notice when a camera stops recording, because that failure is silent until the footage is needed.
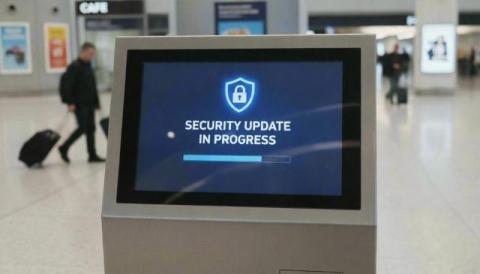
Kiosk Security: Protecting Touchscreens, User Data and Connected Systems

Visitor check-in terminals, retail information kiosks and transport ticket machines make connected technology accessible to the public. Their screens may provide access to business services, while their applications collect personal information or process transactions.

From Runtime to Pre-Change Review | Garrett Hamilton x Jonathan Brucato

Much of security work happens at runtime, finding issues after a change has already shipped. Garrett explains how Reach is opening its agents through the MCP server so teams can ask “what if” before a rule or change goes out. The goal is to give the engineers and change control boards reviewing those changes more confidence before they sign off. In the full episode.

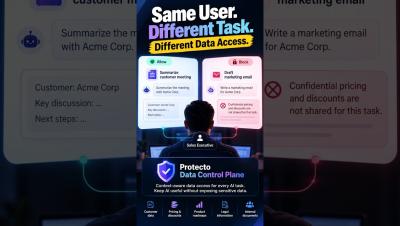
Same user. Same data. Different task. Different access decision. #ai #shorts

A sales executive can view contracts, pricing, discounts, and account details. Ask an AI assistant to summarize a customer meeting, and it needs the customer name. Ask the same assistant to draft a marketing email, and it must not include confidential pricing or discounts. Same user, same data, different task, different answer.

Manage Physical Security with Claude, ChatGPT & Gemini using Brivo's MCP server

What happens when you connect Claude, ChatGPT, or Gemini directly to physical security infrastructure using the Model Context Protocol (MCP)? Traditional portals only answer what they were built to answer - leaving operations and support teams stuck pulling data across a dozen screens. With the launch of Brivo Reseller MCP (the first MCP server for security systems integrators), your AI assistant connects directly to your Brivo partner portal data right alongside your CRM, billing, email, and ticketing tools.

Governing Microsoft 365 Copilot in the Enterprise

Microsoft states the position plainly. Copilot only surfaces organizational data to which individual users have at least view permissions, so it grants nobody access to anything they could not already open. What changes is that material somebody had permission to reach and never would have found now arrives in a summary. ‍ The governance work is therefore permissions work that predates the deployment.

Beyond Compliance: Building an AI Operating Model Using Global Governance Frameworks

By Rob Horne and Parul Dahl, Kroll Cyber Risk EMEA Security Advisory Kroll recently published a series of articles examining governance challenges associated with specific AI implementations, particularly agentic AI and the data, risk and compliance considerations that accompany autonomous decision-making. However, many organizations are now facing a broader challenge.

Shadow AI: When Approved Experiments Create New Shadows

An AI innovation team is asked to build a customer support assistant in two weeks. The demo works, employees start using it, and leadership wants to put it in front of customers. Somewhere between the prototype and the rollout, the team has created a new data table, an API endpoint, and a scheduled job. The project has a sponsor. Does every piece across the customer support assistant have an owner?

10 API Security Best Practices for Achieving PCI DSS 4.0.1 Compliance

PCI DSS 4.0.1 is the first major standard to name API business logic as an attack type you must address. Requirement 6.2.4 lists attacks on business logic, including attempts to abuse or bypass application features through the manipulation of APIs, alongside injection and access control flaws. The timing matters. All requirements, including the ones that were future-dated, have been mandatory since 31 March 2025. Your next assessment will test controls that were optional a year ago. The reason is simple.