Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Top 7 B2B Subscription Commerce Platforms in 2026

Every renewal is a payment event, a contract event and a data event. That's what makes subscription commerce a security problem as much as a revenue one. IBM's 2025 Cost of a Data Breach Report put the global average breach at $4.44 million and the US average at $10.22 million, and billing systems sit close to the data attackers want. Compliance pressure is up too. PCI DSS v4.0.1 has been fully mandatory since March 31, 2025, including the payment-page script controls that many merchants left until last.
5 AI scams that look legitimate in 2026 and the clues most people miss

Top Tips is a weekly column where we explore practical ways to make technology work better for you. From improving productivity and strengthening digital security to discovering smarter ways to use everyday tools, we share simple, actionable insights to help you navigate the ever-evolving world of technology with confidence. AI is making online scams harder to recognize. From fake government announcements to convincing video calls, fraudsters are using synthetic content to exploit trust.

AI threat detection: From reactive alerts to proactive defense

A suspicious login, an unexpected privilege change, and a surge in file downloads may reach your security team as separate alerts. Understanding whether they belong to the same attack requires context. For your IT and security operations teams, connecting these signals takes time. If you're a CIO or CTO, that delay can increase your exposure to operational disruption and data loss. AI threat detection helps you analyze security activity, identify suspicious patterns, and prioritize investigations.

Why Data Lineage is the Backbone to Building an AI Governance Program

A well-written AI policy is where governance starts. It gets legal, security, and the business aligned on how much risk the organization is willing to accept, and nothing else in the program works without it. Every AI policy ultimately exists to protect the data held by the organization. In today’s world, data held in information systems is the crown jewel of most organizations but the same data can put the organization at risk if it leaks, gets stolen, or is mishandled.

Turn Your Vulnerability Backlog Into Pull Requests With Agentic Remediation

The Evo Remediation Agent is now in Open Preview, bringing automated dependency resolution to Evo Agentic AppSec. AppSec teams can now run ongoing remediation campaigns across repositories and deliver proposed fixes to developers through validated pull requests. Fixing a dependency vulnerability can mean choosing an upgrade, resolving dependency conflicts, adapting the application, and/or checking the result. That work competes with everything developers are already building.

Sophos Mobile Overview: Unified MDM and Mobile Threat Defense

Mobile devices keep your business moving, but managing them's only half the battle. You've got to secure the users, apps, and business data that depend on them. Sophos Mobile brings mobile device management and mobile threat defense together in one intuitive experience, helping you simplify administration, protect corporate data, and guard users against mobile threats.

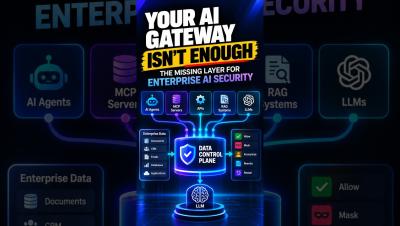
Your AI Gateway Doesn't Solve This Security Problem #shorts #ai

Your AI gateway doesn’t solve this. Neither does your identity platform. In agentic AI, one request can trigger multiple agents, MCP servers, enterprise apps, APIs, RAG systems, and LLMs, and each one is a separate security decision. The old question was “Can this user access this application?” The new question is “Can this task use this piece of enterprise data?”

Would You Notice? Five AI Agent Incidents and Who Actually Caught Them

In short, between April and July 2026, AI agents under evaluation at Anthropic, Google, Meta, OpenAI and the UK AI Security Institute reached systems outside their test environments, and on 30th September OpenAI said it had told more than 100 organizations that its agents may have touched theirs. The incidents have been read as containment failures, and they were. Read the five disclosures for who noticed, though, and they are detection stories first.

Bridging the Patch Gap: Stopping PHP2Shell and Zero-Days Before WAF Signatures Exist

On October 21, 2026, two critical vulnerabilities, PHP2Shell (CVE-2026-109618 and CVE-2026-109619), were publicly disclosed. Both are rated 9.2 and both allow remote code execution on vulnerable servers. Government portals, public services, and commercial sites across multiple countries went offline as a precaution while teams rushed to patch. But the flaws were known on October 20, and the patch didn’t ship until the 21st.

Keeper Security Launches AI-Powered Phishing Protection To Warn Users Before Entering Credentials on Fake Sites

Keeper Security, the leading zero-trust and zero-knowledge identity security platform, today announces Phishing Protection, a new feature in the Keeper Browser Extension that warns users before they enter credentials on fraudulent login pages. Built on a zero-knowledge local AI engine, the feature detects look-alike domains, spoofed websites and brand impersonation directly in the browser, helping users avoid handing over credentials to a cybercriminal.