Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why AI Text Detectors Fail and What to Use Instead

Somebody in the organization will eventually propose running documents through an AI text detector. The instinct is reasonable and the method is the one approach the published evidence rules out, for reasons a security or risk function should understand before the policy gets written. ‍ The organization that built the most widely used language model tried this and withdrew its own tool after six months. Its reason was accuracy, and the figures it published before withdrawing explain why. ‍
Featured Post

The Key to Agentic Security is not to Secure the Agent

In September 2024, OpenAI announced o1 and updates to its Assistants API. Looking back, this marked a shift in how AI systems would be used. These systems were no longer just generating answers. They were starting to connect with tools and affect the world directly. Tool use had previously been possible, but it was clunky and unreliable. Now, it is becoming a native capability. Yet this new ability has arrived before the underlying models have become trustworthy. Real-world capability is being handed to systems whose outputs cannot always be relied upon.

7 Modern Car Safety Features to Compare Before Making a Purchase

Buying a car involves more than comparing prices and comfort. Modern cars have safety technologies that help drivers spot dangers and avoid crashes. However, two cars that seem similar may perform differently due to their sensors and software. Understanding these differences can help you make better choices. Some technologies actively assist in dangerous situations, while others only provide warnings. Comparing independently tested safety features can show you which systems offer real protection and which might have hidden limitations you won't notice during a short test drive.

Every AI Agent Creates Security Debt. Most Organizations Aren't Tracking It.

Technical debt accumulates when organizations prioritize immediate speed and defer the architectural work that keeps systems dependable. Most engineering leaders know how that story ends. The shortcuts that made the first release possible eventually slow down every release after it. The agentic enterprise is creating a security equivalent.

How to Block Sensitive Data in AI Prompts at the Endpoint

A data loss prevention (DLP) team writes a rule to keep customer records out of ChatGPT. The rule catches an uploaded spreadsheet but misses the same records pasted into a prompt, because no file transfer occurred. The team adds text pattern matching to close the gap, and the rule starts flagging harmless prompts that happen to contain a name and a number. Both failures share one cause. The rule judges what the text looks like and cannot see where it came from.

The Impact of AI on CVEs: Industry Challenges

Integrating artificial intelligence into cybersecurity has fundamentally changed vulnerability research – and not necessarily for the better. For decades, discovering and verifying Common Vulnerabilities and Exposures (CVEs) required deep technical expertise, creating a disciplined process that kept disclosure volume relatively manageable. Today, Generative AI has obliterated that barrier to entry.

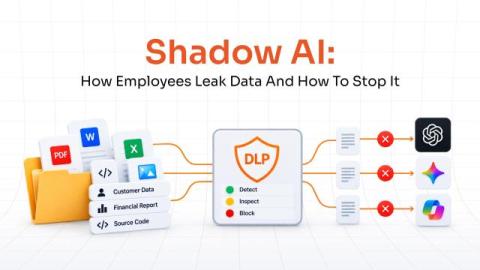
Shadow AI: How Employees Leak Company Data Into AI Tools and How to Stop It

Shadow AI refers to the use of artificial intelligence tools, applications, models, or AI-powered features without the organization's required IT approval, security review, or governance. It is often associated with employees using personal accounts for tools such as ChatGPT or Gemini. However, Shadow AI extends well beyond public AI chatbots.

How to Measure AI SOC ROI: Beyond Hours Saved

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

Cato AI Endpoint secures browser AI, desktop AI and coding agents on every endpoint

AI used to live in a browser tab. Today it also runs inside the apps employees use every day, like Copilot in Word, in dedicated apps like ChatGPT and in coding agents such as Claude Code, Codex and Cursor. Coding agents work differently from chat apps. A chat app answers a question and waits. A coding agent is given tools and takes actions on its own, with the developer’s access. So every endpoint is becoming an agentic endpoint.