Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

PHP2Shell vs. Log4j: Understanding the Risk and Exposure | Bitsight Webinar

Could PHP2Shell pose a cybersecurity risk on the scale of Log4j? Newly disclosed critical PHP vulnerabilities are raising concerns about widespread exposure across enterprise environments and third-party supply chains. With millions of potentially affected systems and limited patching options for legacy PHP versions, security teams face a complex remediation challenge.
PHP2Shell Didn't Break the Internet (Yet)

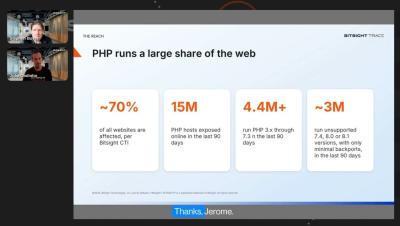
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) arrived with predictions of a Log4Shell-scale mass exploitation event. Panic was visible, many rushed to update or even disconnect systems from the Internet until a patch was applied. PHP runs a large share of the web and the vulnerable ranges were reported to cover every branch from 5.4 to 8.5, which are essentially the majority of versions we can see deployed in the internet installed base.

'Node2Shell' vulnerability (CVE-2026-111497) in active exploitation

On October 21, 2026, Node.js released updates to address multiple vulnerabilities, including an issue in Brotli decoder (CVE-2026-111497). This critical buffer overflow vulnerability (CVSS score of 9.2) has become widely known as Node2Shell but has also been referred to Broccoli2Shell and HTTP2Shell. The issue exists in the Brotli decoder (c/dec/decode.c) in multiple Google Brotli versions, and products that rely on Brotli implementations are vulnerable.

Is My Organization Exposed to PHP2Shell? See It in Aurora Vulnerability Management

PHP2Shell is two unauthenticated remote code execution (RCE) flaws with public exploit code. As AI speeds up the path from vulnerability to exploit, security leaders keep asking two questions. Are we exposed? And what do we fix first? This walkthrough shows how Aurora Vulnerability Management from Arctic Wolf answers both.

PHP2Shell is in CISA KEV: why runtime visibility matters

Five days after PHP shipped the fix, CISA added both PHP2Shell flaws to its Known Exploited Vulnerabilities (KEV) catalog. Federal civilian agencies have until October 29 to remediate. Last week’s question was whether attackers could turn the flaws into working shells. This week’s question is which of your images and hosts still run an affected PHP build, and who can fix each one.

Ep. 91 - PHP2Shell: The PHP Flaws That Can Run a Stranger's Commands Before Your App Even Loads

PHP2Shell is two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, that can let a stranger run commands on your web server without logging in. On Apache mod_php, it can happen before your application code even loads. We unpack which PHP setups are exposed, why PHP says updating is the only safe fix, what to do about end-of-life PHP, and three questions every CISO should ask about a web-tier foothold. Update: on 26 Oct, researchers reported the first successful in-the-wild exploitation.

PHP2Shell Won't Be the Last. Here's Where the Next One Will Show Up First.

On October 17, Amazon's honeypot network logged a PHP2Shell exploitation attempt from an anonymized IP address. Yet, public disclosure was still four days away. By the time PHP got its fixes in on October 21, the technical details had already leaked, proof-of-concept exploits were in wide circulation, and more exploit attempts were being logged left and right.

PHP2Shell: what CYJAX is seeing as attackers chase the leaked PHP flaws

PHP2Shell is a pair of critical PHP flaws that leaked before disclosure and drew instant interest from attackers. This post covers what CYJAX analysts have seen on cybercriminal forums and code repositories, and what organisations running PHP should do now.