Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CrowdStrike Protects Customers from Threats Delivered via PHP2Shell

Two critical memory-corruption remote code execution (RCE) vulnerabilities, collectively dubbed PHP2Shell, have been disclosed in core PHP, the underlying engine powering a vast portion of the web. The CrowdStrike Falcon platform provides out-of-the-box visibility and detection coverage for post-exploitation activities of both vulnerabilities.
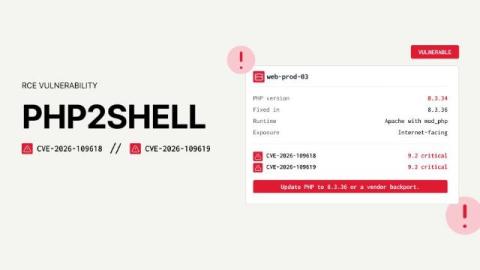
PHP2Shell: Responding to CVE-2026-109618 and CVE-2026-109619

If you run PHP anywhere in your environment, patch to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now. Two critical flaws disclosed this week, CVE-2026-109618 and CVE-2026-109619 (nicknamed "PHP2Shell"), let an unauthenticated attacker run code on a server with nothing more than a crafted web request. Both carry a CVSS v4.0 score of 9.2, every earlier release is affected, and exploitation in the wild has been reported. The patch is the easy part.

CVE-2026-109618 and CVE-2026-109619 (PHP2Shell): Two Critical PHP Remote Code Execution Flaws

The PHP security team has announced an emergency security release for Wednesday, October 21, 2026 at 14:00 UTC. It addresses two critical vulnerabilities, both rated CVSS v4.0 9.2. The vulnerabilities are tracked as CVE-2026-109618 and CVE-2026-109619. Both bugs are described as remote code execution issues, meaning an attacker could get their own commands running on a vulnerable server. The route to disclosure was messy.

Compromised LiteLLM 1.107.0 on PyPI Ships a Credential Stealer and Code Loader

On October 21, 2026, a malicious release of litellm, the Python library and proxy for calling LLM provider APIs, was published to PyPI as version 1.107.0. All seven compiled wheels carried three extra files that install straight into the root of site-packages: a.pth hook that runs a credential stealer every time Python starts, and a sitecustomize.py that starts a background loader built to fetch and run remote Python code every hour. The package has had more than 92 million downloads over the past month.

PHP2Shell: the fix is a runtime upgrade, not a code change

On October 21, 2026, PHP released 8.5.12, 8.4.27, 8.3.36, and 8.2.35 to close two critical remote code execution flaws in the PHP runtime. Both are rated CVSS v4.0 9.2. Together they go by the name “PHP2Shell.” The flaws sit in PHP itself, not in any application built on it. A secure codebase running on an affected PHP build is still exposed. That makes this an inventory problem first and a patching problem second.

Appknox MCP: Find, Fix and Verify Mobile App Vulnerabilities Without Leaving Your IDE

Appknox MCP agent connects your AI coding agent to your Appknox scan results and KnoxIQ analysis. Your agent triages findings by exploitability, fixes the code in your repo and verifies each fix with a re-scan, inside Claude Code, Cursor, GitHub Copilot, Codex or Windsurf. Your AI coding agent already writes features, refactors code and fixes bugs. It can't see your security findings. So when a scan flags a vulnerability in your mobile app, the fix still starts by hand.

CVE-2026-94244: Missing Authorization in Wallet System for WooCommerce

Vulnerability: Missing Authorization Leading to Store-Wide Customer Data Exposure via Exported Wallet Transaction File Vulnerable Version: < 2.8.0 Patched Version: 2.8.0 CVE: CVE-2026-94244 CVSS: 4.3 (Medium) AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N CWE: CWE-862 (Missing Authorization) → CWE-200 (Sensitive Information Disclosure) On 02/09/2026, a security researcher at Astra Security found a Missing Authorization vulnerability in Wallet System for WooCommerce, a popular WordPress plugin by WP Swings that

Cloudflare Responds to Critical PHP RCE Vulnerabilities: Why WAF Enforcement Matters

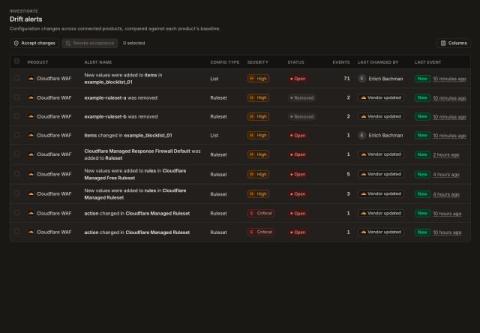
Two critical PHP vulnerabilities have been disclosed, potentially exposing millions of web servers to remote code execution. Cloudflare has already responded by deploying emergency WAF protections. For Reach customers using Cloudflare WAF, Reach Drift automatically detected the new rules and confirmed they were enabled and configured to block malicious traffic.

Arctic Wolf Labs: Finding, Prioritizing, and Patching PHP2Shell Exposure

On Tuesday, October 20, threat actors gained advance visibility into two critical PHP vulnerabilities after details leaked ahead of the planned disclosure, accelerating the race between defenders and attackers. The flaws are tracked as Common Vulnerabilities and Exposures (CVE) identifiers CVE-2026-109618 and CVE-2026-109619. Together they’re known as PHP2Shell. Both carry a 9.2 rating on the Common Vulnerability Scoring System (CVSS) version 4.0 scale.

AI Is Calling In Every Risk You've Accepted: Seven Insights From The AI Security Panel: Unfiltered

On October 14th, the afternoon before the AI Security Summit (AISS) flagship event in San Francisco, Snyk hosted The AI Security Panel: Unfiltered. Yahoo Finance's Deirdre Bosa moderated four people who see AI security from very different seats.