Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Just Shrank the Time Hackers Need to Weaponize Your Vulnerabilities

The Five Eyes intelligence alliance—NSA, CISA, GCHQ, Australia's ASD, Canada's Cyber Centre, and New Zealand's GCSB—just issued a joint warning: AI has compressed the window between vulnerability discovery and exploitation from years to months. Adrian breaks down what the "AI Shift in Cyber Risk" statement actually means for patching timelines and attacker sophistication—and why most organizations aren't moving fast enough to keep up.

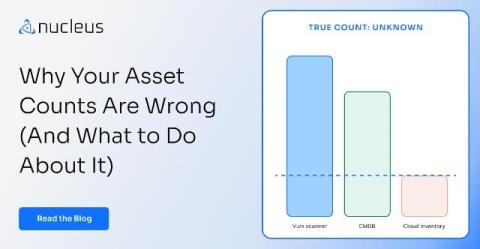
Why Your Asset Counts Are Wrong (And What to Do About It)

If you've ever pulled an asset count from one tool and compared it to another, you've probably noticed they don't match. The discrepancy isn’t minor, either. The difference is likely to be substantial. One scanner says you have 4,200 assets. Your CMDB says 3,800. Your cloud inventory says 1,100. None of them agree, and none of them are right. That's not a data hygiene problem you can solve with a spreadsheet cleanup.

Brace Yourself: Denial-of-Service in a Billion-Download Dependency

brace-expansion is a very popular npm package with over 38 billion all-time downloads (yeah, over 38,000,000,000) and used by tooling almost every JavaScript project relies on - eslint, glob, and npm itself. Despite being in the public eye for a while, we found a new Denial-of-Service vulnerability that could affect millions. This post walks through what the package does, existing issues that were fixed, and the new one we found - CVE-2026-13149.

Critical Remote Code Execution Vulnerability in libssh2 Client Library Require Urgent Mitigation

A suite of severe vulnerabilities has been disclosed in libssh2 (an SSH client library widely embedded in software such as curl, Git GUI clients, PHP, backup tools, and many IoT/embedded devices). The most critical, CVE-2026-55200 (CVSS 9.2/9.8), is a memory corruption bug in libssh2’s ssh2_transport_read() triggered by a malicious SSH server pre-authentication via a crafted packet_length.

CVE-2026-48558: Critical Authentication Bypass Vulnerability in SimpleHelp RMM Exploited for Credential Theft and Malware Delivery

CVE-2026-48558 is a critical authentication bypass vulnerability in SimpleHelp Remote Monitoring and Management (RMM) software, caused by improper validation of OpenID Connect (OIDC) token signatures. When OIDC is configured with group-authenticated login settings, unauthenticated attackers can forge identity tokens to bypass multi-factor authentication and gain privileged technician-level access to vulnerable SimpleHelp servers — without valid credentials.

Browser Security: Zero-Days Are Only Part of the Problem

The browser is the operating environment for modern work — it’s where employees access email, SaaS applications, collaboration tools, HR systems, finance platforms, customer data, developer resources and AI services. All of this activity makes the browser a high-value target for attackers because it sits between users, identities, applications, and sensitive enterprise data.

Azure Monitor Agent Metrics Extension Vulnerability: From Engagement to CVE

This article was authored by Cristhian Parrot from the Kroll Offensive Security Team. Kroll’s Offensive Security Team recently discovered a new vulnerability within Microsoft’s Azure Monitor Agent Metrics Extension, which demonstrates how subtle configuration issues can introduce significant security risks in widely deployed infrastructure components.

CVSS Scoring Issues: Why Your Score is Lying to You

Modern exposure management has evolved beyond vulnerability scanning and alert volume into a discipline focused on measurable risk reduction. As the exposure management market matures, security leaders are adopting cyber exposure management platforms that unify signals across vulnerability, cloud, application, and attack surface tools to prioritize what truly matters.