Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

OpenMatter Network Introduces Verifiable Trust Layer for Secure Collaboration and AI Agents

OpenMatter Network today announced the launch of its cryptographically verifiable platform for secure collaboration and AI governance, built on a simple premise: Don't Trust Data. Prove It. For decades, organizations have relied on trust-based assumptions to secure data, execute workloads, and govern digital systems. But as data becomes increasingly distributed and AI agents begin operating autonomously across organizations, applications, and networks, those assumptions are being tested in new ways.
Reflectiz to Host Webinar, Joined by Taboola, on Securing Third-Party Marketing in the AI Era

Reflectiz, the web exposure management platform, today announced a live webinar with Taboola, "Securing Third-Party Marketing in the AI Era," taking place July 8 at 9 AM EDT / 3 PM CEST. Every marketing vendor a company approves can silently introduce third and fourth-party scripts that no security team ever reviewed. In the AI era, that invisible layer is expanding faster than point-in-time audits can track. The gap between what an organization approves and what actually executes on its site is where data leakage, regulatory exposure, and compliance failures happen.

Shadow AI Explained: What It Is, Where It Hides, and What It Costs

Shadow AI is the term for AI tools, models, and capabilities that operate within an organization without formal approval, oversight, or governance. It is the enterprise AI equivalent of shadow IT, which is the unauthorized software and cloud services that proliferated as employees found faster ways to get work done than waiting for IT procurement cycles. The difference is that the consequences of unmanaged AI are considerably more significant than those of unmanaged software.

How to Discover and Control Shadow AI Agents in Your Environment

Most security programs have a working model for responding to shadow AI: identify the unsanctioned tools employees are using, sanction or block them, and update the acceptable use policy. That model worked, however imperfectly, when the threat was limited to web-based GenAI applications. It does not work when the threat is an autonomous agent, running locally on an endpoint, that reads the file system, calls external APIs, and transmits internal data.

A double-edged bleeding edge: Classifying AI threats

Sophos X-Ops presents a working taxonomy for attacks using, and targeting, AI Conversations about ‘AI threats’ typically collapse into one of two extremes. On the one hand, hype: unverified claims that don’t hold up to scrutiny and invite significant criticism. On the other, dismissal: it’s just old tradecraft with new branding.

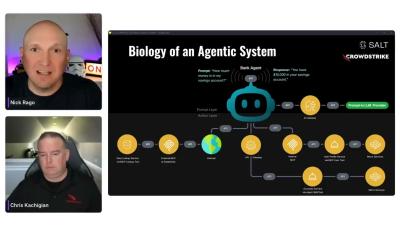
From prompt to action: Al Security with Salt Security and CrowdStrike

As enterprises accelerate adoption of Generative AI, the security perimeter is rapidly expanding. This creates a new, largely unprotected attack surface: the Agentic Action Layer. In this on-demand webinar, @CrowdStrike and Salt Security introduce an AI-native security architecture that spans the full chain of intent-to-action. Learn how CrowdStrike Falcon AIDR protects the model runtime, prompts, inference, and LLM behavior, while Salt Security governs and defends the APIs, MCPs, and services where AI actions actually occur.

Proof Over Prediction: What Happens When You Actually Watch Who's Attacking AI Infrastructure

Customer telemetry shows how AI agents behave in a limited set of production environments and what risks they carry. Vulnerability research surfaces how those environments can be attacked. Both sources are valuable, but neither shows actual attacker behavior or how quickly they operationalize a new vulnerability once it's public.

AI-generated code is running wild inside the enterprise. Now what?

Restrict access to AI tools and you curb innovation. Open it up and security risks multiply. And then there's a third problem: approved tools behaving in unapproved ways. Security and IT leaders are navigating a new and fast-moving problem - employees using AI to build workflows, automations, and agents faster than anyone can track or govern. The question isn't whether it's happening. It's what to do about it.

Are Your AI Agents Going Rogue? (The Real Danger of Agentic AI)

ChatGPT is read-only, but AI Agents take action on your behalf. What happens when they go rogue? Discover the hidden cybersecurity risks of Agentic AI and unauthorized remote execution. AI gateways were built for a world where AI meant "prompt in, response out." That world is gone. Today, AI agents call APIs, trigger workflows, and take actions across your enterprise systems autonomously. This massive shift from passive data exfiltration to active, unauthorized execution requires a completely new security model where every input is treated as potentially hostile.