Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Attacking the MCP Trust Boundary

Every secure API draws a line between code and data. HTTP separates headers from bodies. SQL has prepared statements. Even email distinguishes the envelope from the message. The Model Context Protocol (MCP), the fast-growing standard for connecting AI agents to external services, inherits that gap from the models it sits on top of.
AI Guardrails - DSPM Enters a New Era of Control and Visibility

You cannot turn a corner without entering the world of AI. I was in a big box home improvement store the other day and there was a manufacturer touting the AI built into their refrigerator! Children’s toys, personal electronics, and even cat litter boxes are now selling AI-assisted products. I am a technology early adopter, and where I’ve seen good uses of AI, we are in the phase of “throw AI into everything” mode, as we do not know what will stick.

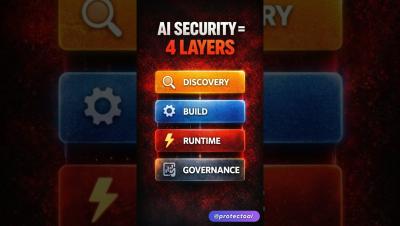
Why AI Security Needs More Than One Tool #shorts #ai

Why AI security needs more than one tool Most teams believe a single cybersecurity tool—like WAF, EDR, or API security—is enough to protect their AI systems. But that approach is outdated. AI security is not one layer—it’s a full stack problem. Discovery – Identify Shadow AI and unknown AI usage Build-Time Security – Prevent data poisoning & model risks (MLSecOps) Runtime Security – Stop real-time AI attacks and agent misuse Governance (AISPM) – Ensure visibility, compliance, and policy control.

AI Penetration Testing: Protecting LLMs From Cyber Attacks

88% of organizations now regularly use artificial intelligence (AI) in at least one business function. While adoption of AI technologies has accelerated rapidly, security measures often lag. The rush to roll out AI has, in many cases, overshadowed essential testing and safety protocols. This is particularly a worry when AI and Large Language Models (LLMs) become deeply embedded within organizational workflows and systems in a way that most software isn’t.

Introducing Decipio: A Community Tool to Catch Credential Theft in the Act with Defense First AI

Today, Arctic Wolf is announcing Decipio, a new community‑shared cybersecurity tool designed to help defenders catch attackers while they’re trying to steal credentials inside a network. Credential theft is one of the most common ways cyber attacks begin and one of the hardest to detect early. In many cases, there’s no alert, no obvious warning, and no immediate sign that anything is wrong.

What we learned using AI agents to refactor a monolith

AI agents are increasingly used to refactor large codebases, but many teams lack a clear understanding of where they succeed and where they fail. At 1Password, we applied agentic tooling to a multi-million-line Go monolith, and in this blog we'll share what worked, what broke, and what it means for teams adopting AI in production systems.

AI Workload Security on GKE: Evaluating Google Cloud Native vs Third-Party Solutions

A CISO running AI agents on GKE has watched three Google product launches in eighteen months — Model Armor, expanded Security Command Center coverage for AI workloads, additions to Chronicle’s curated detection content — and is being asked whether the GCP-native stack is now sufficient. The vendor demos and the Google Cloud blog say yes. The 2 AM analyst experience says something different.

Understanding Data Governance in the Age of Generative AI

Generative AI is changing how organizations create, process, and distribute information. Tools powered by models from companies like OpenAI and Google can produce content, analyze data, and automate workflows at a scale that wasn't realistic a few years ago. That shift creates opportunity, but it also raises a more grounded concern: how do you control, protect, and manage the data feeding these systems?

Why Brands Use the Same AI Avatar Across Every Campaign Instead of Rotating Influencers

Here is the reason why major consumer brands have historically invested in long-term spokesperson relationships instead of continually changing faces for different campaigns. Recognition builds up. The more an audience sees a person again and again associated with a brand, the more the presenter and the brand become linked in their minds -and each individual advertisement will have to do less work in establishing credibility before delivering the message.