Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Application Security including monitoring, testing, and open source.

AI Pentesting for Compliance

For two decades, “penetration testing” has meant the same thing: once a year, you hire a firm, a human tester spends a week or two on your systems, and you get a PDF. Most compliance frameworks were written around exactly that ritual, a slow, manual, point-in-time engagement. Software doesn’t ship once a year anymore. It ships many times a day.
And another one. GitHub ships break-glass credential revocation

Last week, GitHub released self-service credential revocation for Enterprise. The feature lets organization owners cut off compromised credentials across the entire organization in one action instead of trying to track down individual tokens during an active incident. This fix was a long time coming, as the past few months have shown what happens when revocation is slow or incomplete.

Top 10 Application Security Risks (2026 Edition)

You already know the threats are getting worse. What’s harder to articulate — especially to leadership — is exactly how they’re getting worse, and what’s slipping through the cracks in your current program. The application security risks your teams face in 2026 are not just more numerous than they were five years ago; they’re structurally different.

npm now freezes high-impact accounts after risky account changes

npm shipped a new protection this week for its most depended-on accounts. When npm detects a sensitive action on a high-impact account, like an email swap or the use of a 2FA recovery code, it puts that account into a 72-hour read-only state and sends an alert to the previous email address. The package installs and downloads keep working as normal during this time, and the freeze lifts automatically at the end of the waiting period.

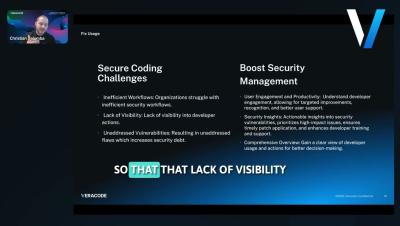
Boost Security Workflows with Veracode Analytics | Secure Coding Challenges & Solutions

Struggling with inefficient secure coding workflows, lack of visibility into developer actions, and growing security debt? In this clip, Christian Dalomba breaks down the biggest challenges organizations face with secure development and shows how Veracode Fix Analytics helps you move beyond just finding vulnerabilities to actually fixing them faster and smarter. Key takeaways.

Compromised GitHub action codfish/semantic-release-action steals CI/CD secrets

On Jun 24, 2026, the codfish/semantic-release-action GitHub Action was compromised through an imposter commit attack. An attacker force-pushed two malicious commits into the repository and repointed sixteen tags to them, including the floating major version tags v2, v3, v4, and v5. Any workflow referencing the action by one of those tags will pull and run the attacker's code on its next CI run.

Aikido x Drydock | A way for maintainers to catch malware before it ships

Maintainers, this is for you. We're partnering with Drydock so maintainers can see exactly what's inside a package before they approve it, catching malware before it ships instead of disclosing it after. Drydock lets you read the actual bytes of a staged release before it goes live, so bad versions get caught at approval rather than in a post-mortem. For npm and PyPI maintainers, Drydock is available at no cost.

Application Security Already Knows What's Broken. Context Is How You Fix It Faster.

While traditional security tools excel at finding vulnerabilities, the sheer volume of alerts—now accelerated by AI-driven development—has made manual triage impossible. The true value of Application Security Posture Management (ASPM) lies not in providing more visibility or creating a cleaner backlog, but in shifting from cataloging risk to taking fast, context-driven, machine-speed action to actually fix what is broken.

Over 140 popular Mastra npm Packages Hit by Supply Chain Attack

On June 17th we detected a large-scale supply chain attack targeting the entire @mastra npm scope, a popular open-source AI agent framework. An attacker republished 141 packages in a burst between 01:15 and 02:00 UTC, silently injecting a malicious dependency into every one of them. The affected packages include @mastra/core, which has 918K weekly npm downloads, as well as mastra and create-mastra.

Cyber Sessions with Sohail Iqbal, CISO at Veracode | CSO Cybersecurity Conference & Awards

As AI accelerates software development at machine speed, security teams are struggling to keep up with remediation. In this insightful interview, Veracode CISO Sohail Iqbal breaks down the security realities of AI-assisted coding and shares how organizations can close the growing gap between code velocity and secure deployment.