Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Agent Incident Response: Containment Is the Easy Part

Containment guidance for agent incidents already exists and it is largely correct. Revoke the tokens, freeze the orchestration tier, cut egress, set the vector store to read-only. Those steps take minutes and any competent team will find them. ‍ The difficulty sits either side of containment. Deciding what kind of incident this is takes longer than stopping it, establishing what the agent did before you stopped it takes longer still, and both depend on preparation that has to exist beforehand.

Steps to Recover from Ransomware Attacks Efficiently

A ransomware attack can stop business operations in a very short time. Files may become locked, systems may go offline, and employees may lose access to important tools. In some cases, attackers may also steal data before blocking access to it. Recovering from ransomware takes more than simply restarting computers. Businesses need a clear plan for containment, investigation, data recovery, system repair, and future protection. A rushed response may make the damage worse or allow attackers to return.

How to Improve MTTR: A Practical Guide for Security Teams

A critical alert enters the SOC queue during the overnight shift. By morning, the dashboard shows an acceptable headline MTTR because the incident was closed quickly after an analyst finally picked it up. The timeline tells a different story: the alert sat unassigned for nine hours because severity routing sent it to the wrong queue. The team optimized the visible number while leaving the dangerous delay untouched.

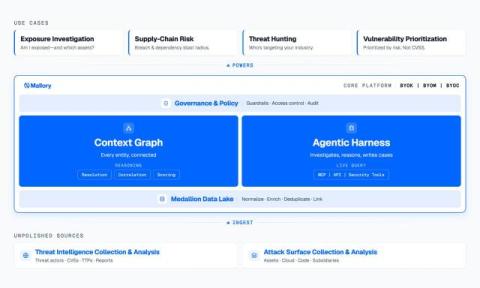
Mallory Unifies Threat Intelligence, Exposure Context, and Response Into One Architecture for Security Teams

As AI-assisted attackers compress exploitation timelines to hours, Mallory turns live adversary intelligence into prioritized, policy-governed action across the tools security teams already run.

How Clear Communication Strengthens Cyber Incident Response

When a cyber incident hits, your team's technical skills are definitely put to the test. But beyond the digital forensics and system recovery, another skill's just as important for getting through it: communication. Good communication is the backbone of any successful incident response (IR) strategy, but people often don't think about it until it's too late. This guide will show you how to build a clear communication framework for your IR team.
Featured Post

Security on a reactive budget

Ask most security leaders how their last significant budget increase came about, and the honest answer is rarely "we made the case and won it." It's usually "something happened." A breach, a near-miss, a competitor's headline, an audit finding that couldn't be ignored or a new regulation with a deadline attached. Security spend still moves in response to events far more often than it moves in response to argument, and that has quietly shaped how the function operates: always slightly behind the risk, always justifying itself against the last incident rather than the next one.

Security Strategies That Help Minimize Data Breach Risks

Data compromises happen daily, creating massive headaches for companies of all sizes. Cyber criminals constantly find fresh entry points into modern networks. Smart business leaders focus on proactive defense methods to stay ahead of bad actors. Simple systemic upgrades can keep sensitive customer records safe from harm.

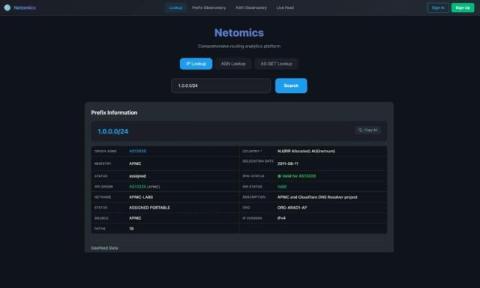
Routing Context: The Missing Piece In Network Incident Response

Ask anyone who has run an incident bridge during a routing event, and they will describe the same scramble. Traffic is going somewhere it should not, alerts are firing, and the team is trying to answer a deceptively simple question: is this announcement legitimate, and if not, whose is it? The tools to answer exist, but they are scattered, and the minutes spent stitching them together are minutes traffic keeps flowing the wrong way.

How Small Businesses Can Build a Secure and Maintainable IT Environment

Small businesses depend on technology for nearly every part of their daily operations. Customer communication, invoices, accounting, document management, online sales, remote work and internal collaboration all rely on computers and digital services. This makes even a small company an attractive target for cybercriminals.