Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Claude Code-powered multi-tenant SecOps for MSSPs | LimaCharlie demo

See how LimCharlie's Agentic SecOps Workspace handles multi-tenant security operations at scale. This demo walks through real-world scenarios that MSSPs face daily: Unlike token-based AI tools that become cost-prohibitive at scale, this platform uses a flat-fee per analyst model. Every capability in your tech stack becomes accessible through AI-powered automation, and you maintain full control with granular permissions.
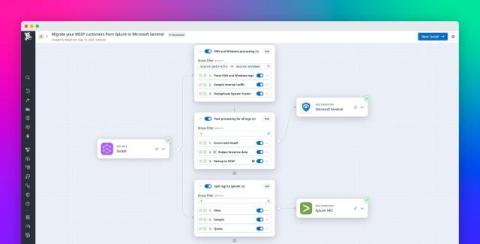
Simplify log collection and aggregation for MSSPs with Datadog Observability Pipelines

Managed security service providers (MSSPs) deliver 24/7 monitoring and incident response for hundreds of customers across large, hybrid environments. As they add more customers and ingest more logs, MSSPs face mounting difficulties in collecting and processing that data before routing it to downstream security tools. Doing this reliably at petabyte scale while accounting for complex, customer-specific taxonomy and compliance requirements is a major challenge.

What Is an MSSP in Cybersecurity? How Managed Security Providers Protect Businesses in Orange County

Cyber threats are no longer limited to large enterprises. Small and mid-sized businesses across Orange County and Anaheim are now prime targets for ransomware, phishing attacks, credential theft, and network breaches. The reason is simple. Attackers know many growing businesses lack in-house security teams, real-time monitoring, and structured incident response plans.

Secure What's Next: How a World-Class MSSP Builds Trust and Scale for 2026

Jesse Emerson, Chief Product Officer at LevelBlue, the world’s largest pure-play Managed Security Service Provider (MSSP), recently sat down to answer a few questions about what makes an MSSP a valuable client resource and how he sees the MSSP’s role changing in the coming year.

LevelBlue Secures a Top Five Spot on MSSP Alert's 2025 Rankings

For the second consecutive year, LevelBlue has been named a top-ranked Managed Security Services Provider (MSSP), placing fifth on the prestigious MSSP Alert’s Top MSSP 250 list for 2025. “LevelBlue is the world’s largest pure-play Managed Security Services Provider (MSSP), offering AI-driven, cloud-native cybersecurity solutions across managed security, MDR, offensive security, strategic advisory, and incident response,” MSSP Alert said.

Sedara Named to MSSP Alert's 2025 List of Top 250 MSSPs

Buffalo, NY — December 15, 2025 — Sedara, a managed security services provider delivering comprehensive cybersecurity solutions for organizations of all sizes, today announced it has been ranked on the MSSP Alert 2025 Global Top 250 Managed Security Service Providers (MSSPs) list. This marks the fifth year Sedara has been recognized as a Top 250 finalist, highlighting the company’s continued presence among leading cybersecurity service providers worldwide.

Hyperautomation Transforms MSSP Cybersecurity Trends in 2026

See how Torq harnesses AI in your SOC to detect, prioritize, and respond to threats faster. Request a Demo Fareed Cheema is the Global Head of Sales Engineering at Torq, leading worldwide pre-sales strategy, execution, and technical innovation. Over the past 3.5 years, he has helped scale Torq’s technical and go-to-market teams while driving customer success in a rapidly changing security automation market.

How Managed Cybersecurity Services Reduce Risk and Enable Business Growth

Today's organizations of all sizes face increasing pressure to protect sensitive data, maintain compliance, and defend against sophisticated cyberattacks. At the same time, they must continue innovating, scaling, and delivering exceptional customer experiences. This dual mandate-security and growth-can feel at odds for many companies.

How MSSPs can automate their way to full-spectrum security

The end of October is here, which means it is time to ask: What have you, as a managed service provider (MSP), learned from Cybersecurity Awareness Month? The most critical lesson remains that human behaviour is the single greatest risk and the single greatest opportunity for defence. While no amount of training can eliminate every mistake (which is why we need automation), a security-aware technician acts as the final, critical filter that can spot novel social engineering attacks and enable fast incident response, but only if the back end is hyper-automated, so technicians know about these potential attacks immediately.