Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Rise of Legitimate-Service Phishing: 1 in 10 Phishing Emails Now Comes From a Platform You Trust

A legitimate sender does not mean legitimate content. Attackers have abused legitimate services such as DocuSign, SharePoint, Adobe Sign, Dropbox and Google Drive to exploit that trust for years. KnowBe4's Phishing Threat Trends Report Vol. 7, released April 2026, flagged this shift at the industry level: 22% of all phishing attacks are now sent through a legitimate platform, with attackers moving from impersonating a brand to abusing that brand's actual infrastructure.
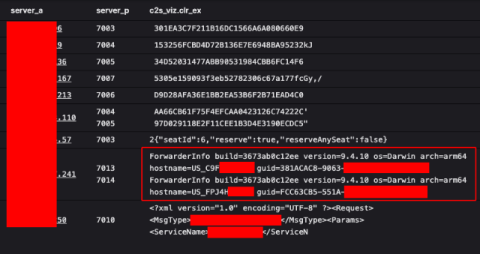
Corelight in the Black Hat USA NOC: A playlist of attendee mistakes

When I got back from Black Hat USA, I was stunned. Of course, it’s easy to be overwhelmed by Black Hat. There is so much going on. Las Vegas casinos are loud and flashy. Going outdoors feels like standing on the surface of the sun. Everywhere you walk there are strong smells, and you hope it’s a delicious meal, but sometimes it’s not.

What is privacy management? Core components and how to build a program

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Egnyte Collaborates With Microsoft to Bring Governed AI to Windows 11

AI agents are moving beyond the browser and into the desktop applications professionals use every day. Egnyte is excited to announce a new collaboration with Microsoft to bring Egnyte AI to Windows 11 through Microsoft Execution Containers (MXC), enabling AI agents to work directly alongside desktop applications while operating within enterprise security boundaries.

SOC metrics that prove your security actually works

SOC metrics are quantifiable measures of how well a security operations center detects, investigates, and contains threats. The metrics that matter most are mean time to detect (MTTD), mean time to respond (MTTR), and incident closure rate, because together they show speed, effectiveness, and reliability, not just activity.

What Is Agentic AI Security: The InfoSec Guide

A conventional AI chatbot answers a question and stops there. An AI agent can plan a sequence of steps, choose which tools to call, use credentials, change systems, and hand work off to other agents, sometimes without a human reviewing each move. Security teams are under increasing pressure to keep pace.

Agent 365: How to Find the Shadow AI Agents in Your Tenant

Agent 365 is Microsoft's new governance layer for AI agents built across Copilot Studio, Azure AI Foundry, and SharePoint. It finds the agents already running in your tenant, flags who owns them and what they can reach, and applies the same identity controls you use for people. Most organizations have more agents out there than they think.

tensorlake NPM package compromised with Shai Hulud worm

On 8 October 2026 a threat actor published a compromised version of tensorlake to npm. The compromised version is 0.5.144 and contains a variant of the Shai-Hulud worm, which exfiltrates secrets from infected devices and attempts to self-replicate through connected supply chains. Tensorlake is a serverless sandbox for AI agents and its npm package has a reported lifetime install count of over 100,000.

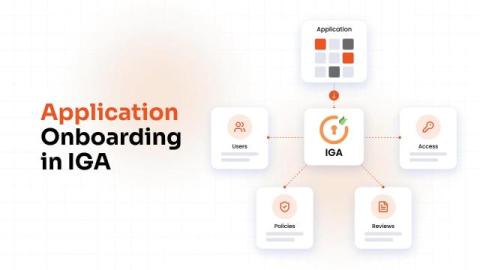
Application Onboarding in IGA: A Practical Guide

Application onboarding is the process of integrating an application with your identity governance and administration platform so its accounts, roles, and entitlements can be governed. Once an application is onboarded, you can: Without onboarding, an application stays outside your controls, and any access inside it is invisible to your security and audit teams.