Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Advanced Settings For Backup Plan - GitProtect.io Tutorial - Git Repository Backup

In this video, we would like to show you how you can create your own custom backup plan for your git (GitHub, Gitlab, BitBucket) organization to fit your needs. Set up encryption, compression, set up when you want the backup to be performed, and many many more in this GitProtect.io tutorial.
GitHub Supply Chain Attacks Highlight the Urgency of Zero Trust SaaS Data Security

In early April, the tech industry witnessed a major GitHub security incident targeting GitHub organizations using Heroku and Travis CI. GitHub was made aware of this threat via an attack leveraging AWS API keys to GitHub’s own npm production infrastructure. As upstream security risks within SaaS platforms become more common, organizations that leverage these platforms are relying on tools like Nightfall to protect themselves.

FROGBOT : Securing your git repository!

Frogbot scans every pull request created for security vulnerabilities with JFrog Xray. With Frogbot installed, you can make sure that new pull requests don’t add new security vulnerabilities to your code base alongside them. If they do, the creator of the pull request has the opportunity to change the code before it is merged. Frogbot reports its findings directly in the git UI. It simply adds a comment with its findings. You can think of Frogbot as your new team member, keeping your code safe.

GitLab Password Security Vulnerability - CVE-2022-1162

On Thursday, March 31, 2022, GitLab released an advisory for a critical password security vulnerability in GitLab Community and Enterprise products tracked as CVE-2022-1162. GitLab is DevOps software that combines the ability to develop, secure, and operate software in a single application. The exploitation of CVE-2022-1162 can allow a threat actor to guess a hard-coded password for any GitLab account with relative ease.

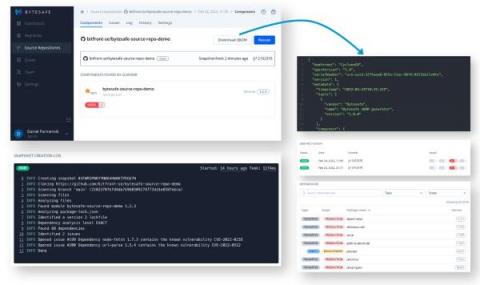
Export and Distribute SBOMs Directly From Your Git Repositories

Guest Blog by Daniel Parmenvik – CEO of bytesafe.dev For many, Software Bill of Materials (SBOMs) have changed from a manual list of assets for due diligence procedures to become an integral and automated part of software development. The ever increasing appetite for open-source software translates into a need to keep track of software assets (or open-source dependencies) for all applications, at any given point in time.

Cloud Threats Memo: Tightening Up Leaky GitHub Repositories

Another day, another cloud service leaking personal data because of a misconfiguration. And before you jump to any conclusions, no, it’s not a leaky bucket on AWS S3 or a public blob on Microsoft Azure… The culprit is, once again, GitHub, where an open-source hardware manufacturer has inadvertently left exposed a private-to-public repository that “could have enabled unauthorized access to information about certain user accounts on or before 2019.”