Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

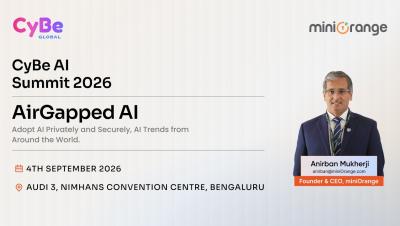
Session on AirGapped AI - Adopt AI Privately and Securely, AI Trends from Around the World at CyBe

In this session at CyBe AI Summit 2026, NIMHANS Convention Centre in Bengaluru, our Founder & CEO Mr. Anirban Mukherji discussed current AI trends, geopolitical and sovereignty risks tied to frontier LLMs, and practical implementations for India. He addressed how AI-driven automation like delivery robots and drones can disrupt jobs, why governments and defense agencies require air-gapped or on-prem solutions, and how cost and restricted access to frontier models create inequity in AI adoption.
How to Hide the Status Bar and the Notification Bar on Android Devices?

Android devices are designed for flexibility. Employees can check notifications, adjust connectivity, open settings, and move between apps with a few taps. That flexibility works well for personal use, but it can introduce distractions, security gaps, and usability issues when a device is dedicated to business tasks.

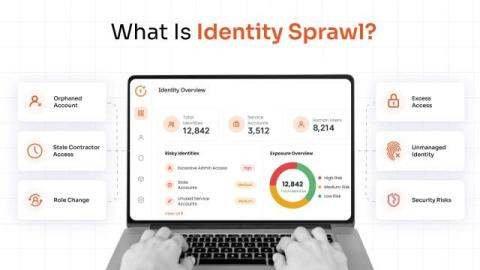
Identity Sprawl: Risks, Causes, and Best Practices for Enterprise Identity Management

An employee leaves the company, but their SaaS account remains active. A contractor still has access to a project workspace months after the contract ends. Someone changes departments and keeps permissions from their previous role. Meanwhile, IT is managing identities, human and non-human across multiple directories, cloud platforms, SaaS applications, and third-party tools. Individually, these accounts may seem insignificant.

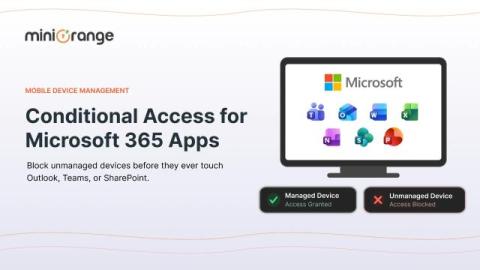
How Conditional Access Protects Microsoft 365 Apps From Unmanaged Devices

Your sales representative logged into Outlook from a coffee shop laptop that isn't enrolled, isn't encrypted, and hasn't seen a security patch in eight months. Should Microsoft 365 let that sign-in through just because the password was correct? That single question is why conditional access exists. Passwords tell you who someone claims to be. They say nothing about whether the device behind that login is safe to trust with your company's email, SharePoint files, or Teams chats.

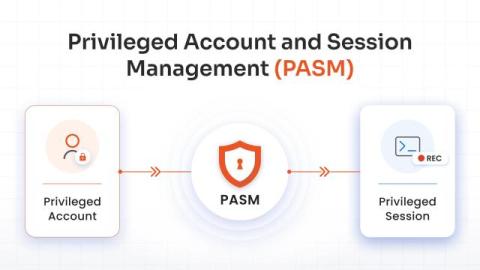
Privileged Account and Session Management (PASM) Explained

Privileged accounts have elevated access that can be used to rewrite system configurations, alter sensitive databases, create new admin users, and exfiltrate confidential customer data. This makes them attractive targets for attackers and risky when poorly managed. Basic passwords and network firewalls aren’t enough to protect them. You need to monitor them continuously. This is where Privileged Account and Session Management (PASM) becomes essential.

Falcon Next-Gen Identity Security: Agentic Identity Provider

CrowdStrike delivers the next evolution of the agentic SOC on the Falcon platform: coordinated teams of expert agents that investigate endpoint, identity, SaaS, cloud, and network domains simultaneously, converging on a single, evidence-backed verdict your team can trust.

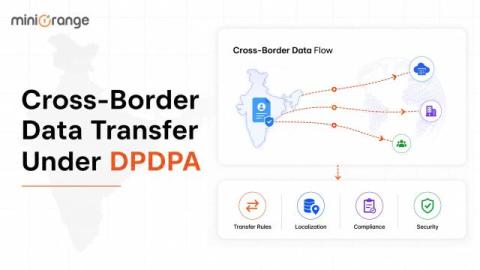
Cross-Border Data Transfer Under India's DPDPA

Businesses operating across countries routinely move personal data between India and overseas systems. Customer information may be stored by a global cloud provider, employee records may be accessed by an international headquarters, or an Indian business may use SaaS platforms whose infrastructure is located outside the country.

ITDR + IGA: The key to 'self-healing identity security'

Curious what an identity threat detection and response (ITDR) system does and why it matters? Rob Kraczek, global strategist at One Identity, breaks down its ability to catch anomalous activity and explains how ITDR and a strong identity governance and administration (IGA) tool have each other’s back, watching the front and back doors attackers use to get in.

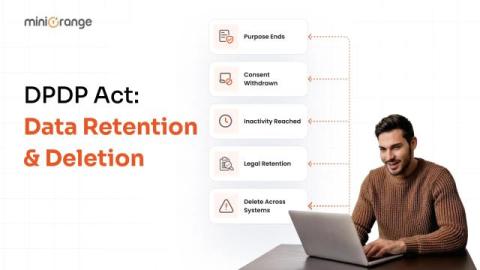
Data Retention Policy Under the DPDP Act: How Long You Can Keep Data and When to Delete It

How long should an organization keep personal data? Under the DPDP Act, the answer is not simply one year, three years, or any other fixed period. The right retention period depends on why the data was collected, whether that purpose still exists, and whether another law requires the organization to keep it.