Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

NIS2 Part One: Why Your NIS2 Supply Chain Strategy Is Already Falling Short

Tens of thousands of European organizations are legally accountable for the security of companies they do not control but on whose services they rely. Under Article 21(2)(d) of the NIS2 Directive, any in-scope entity is required to manage supply chain security, including the security aspects of its relationships with its direct suppliers and service providers. Article 21(3) further specifies that an organization must take each supplier’s specific vulnerabilities into account.
Managing Third-Party Cyber Risks in Complex Supply Chains

Big breaches often start somewhere boring. A refrigeration contractor with remote access to the network (Target, 2013). A file-transfer tool nobody on the security team had thought about in years (MOVEit, 2023). A compression library buried four layers deep in a Linux distro. Meanwhile most vendor reviews still run on an Excel questionnaire that gets filled in once, filed and forgotten, and attackers know that perfectly well.

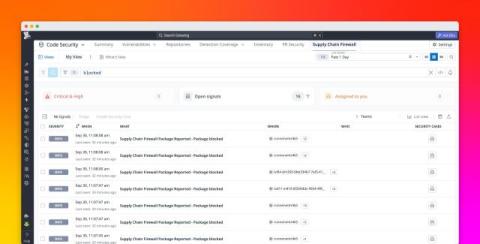
Block malicious packages across your organization with Supply Chain Firewall and Datadog Code Security

Campaigns such as Shai-Hulud 2.0 have demonstrated how quickly package malware can propagate through npm and then harvest credentials. Traditional dependency scanning can identify known risks in code once a package is added to the code, but security teams also need a check before installation.

Why Open Source Is the Easiest Target for Supply Chain Attacks

Attackers targeting open source dependencies already have all the code they need. Curtis Koenig, Head of Application Security at Gen, explains the fundamental asymmetry and why building quality fixes at speed is the real challenge for defenders. "An attacker can produce very fast, very ugly code that propagates through as an attack. When we're trying to fix something, the challenge we have is we're always trying to build for quality.".

The 3 Layers of a Mature Software Supply Chain Security Program

There are lots of terms used to generalize what a mature application security program looks like. Find & Fix. Continuous Remediation. Code to Cloud, Unified Risk. The underlying message in these buzzwords is the same: security needs to be systemic. Defense in Depth is preached as a security best practice by leading cybersecurity agencies like NIST and CISA, and these principles are especially relevant to the metastasizing software supply chain risk seen across enterprises.
Featured Post

Why Data Governance Has Become a Critical Defence Against Ransomware in Healthcare

Ransomware and ransomware-style attacks can have a catastrophic impact within healthcare, where disruption directly impacts safety and continuity. Today's ransomware groups increasingly operate as sophisticated criminal enterprises, sharing tools, infrastructure, and expertise through ransomware-as-a-service (RaaS) models. This lowers the barrier to entry for cybercriminals while allowing experienced threat actors to focus their efforts on identifying and exploiting high-value targets.

December 2026 Is Closer Than You Think: What the UK's Defence Cyber Directive Means for Your Organisation

The UK’s Ministry of Defence has sent a clear message to organisations within the Defence supply chain. By 31 December 2026, all Defence industry partners are expected to achieve Defence Cyber Certification (DCC) Level 0, including Cyber Essentials for all applicable business-critical systems within scope. This represents a significant step in strengthening cyber resilience across the Defence ecosystem and raising the baseline for cyber security throughout the UK’s supply chain.

Extending the Single Source of Truth to the Agentic Software Supply Chain

Every developer on your team now runs multiple agents. None of them are waiting for human sign-off to act. That’s exactly the gap we discussed and closed at swampUP 2026. JFrog unveiled new capabilities that extend the JFrog Platform as not only the Single Source of Truth for OSS and heritage software, but now the Agentic Software Supply Chain. Here’s everything we announced, and why it matters.