Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Cato AI Security: Three Questions to Answer About AI in Your Organization

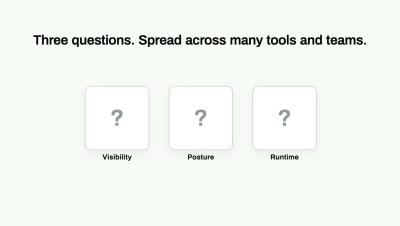
Do you know how AI is used in your organization right now? Cato AI Security helps you answer. AI is in the hands of employees, inside the applications teams build, and running as agents. That leaves security teams with three questions, spread across many tools and teams: which AI is in use, is it set up safely, and can you stop a threat inline? Cato AI Security answers all three on one platform: Cato AI Labs research finds AI-native attacks in the enterprise tools employees already use.
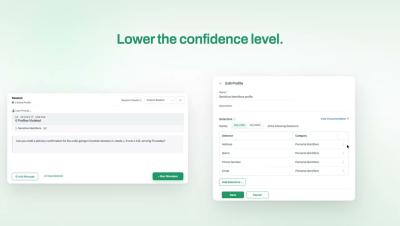
Cato Engine Playground: Test Your AI Detectors Before Production

You've written your AI policies. Now prove they work before you publish them. Security teams build detectors to enforce their AI policies, and they need to see how those detectors behave before they go live. Too strict, and they block work that should go through. Too lenient, and nothing gets caught. The Engine Playground in the Cato Management Application lets security teams test detectors before they go into production.

Securing Agentic Workflows Starts With Data Lineage

A procurement lead asks an AI agent to summarize renewal terms for a software vendor. The agent pulls from a contract repository, a legal team’s chat thread, and a spreadsheet of negotiated discounts. A second agent turns the summary into a briefing and posts it to a shared workspace. No person reviews either handoff. Three weeks later, the vendor quotes an internal walk-away price that was never meant to leave the company.

CrowdStrike Extends the Agentic SOC to Detect and Stop Agent Insider Threats

The most dangerous agent in your environment may be one you already approved. It runs under a real employee's identity, connects to tools their team signed off on, and has the access it needs to do its job. But when something upstream changes, like a tampered tool or an instruction that shouldn't be there, it can drift without tripping an alarm. This is the new insider threat: not an employee, but a trusted agent acting on their behalf.

CrowdStrike Introduces Agentic Adversary Emulation to Counter AI-Enabled Adversaries

Frontier AI is enabling threat actors to rapidly learn an environment, identify weaknesses, and chain them into viable paths to critical systems. These capabilities allow adversaries to move faster while exploiting vulnerabilities, misconfigurations, and other gaps to achieve their goals.

Securing the AI-era network: Why performance and defense now belong together

Secure the AI-era network by combining high-performance protection, deeper visibility across every environment, and coordinated response that stops fast-moving threats sooner. AI doesn’t operate in isolation. Its prompts, workflows, data exchanges, and API calls all depend on the network. As organizations put AI to work, it adds a new layer of traffic that is increasingly encrypted, application-driven, and machine-to-machine.

The Deepfake Episode: AI Avatars, CEO Clones & Likeness | Attempted Intelligence Ep. 4

When AI-generated video floods your feed, how do you train an entire workforce on deepfakes without creating content that feels fake? In Episode 4 of Attempted Intelligence, hosts Harlan Parrott (VP of AI Innovation at KnowBe4) and Matt Duren (SVP of Engineering for AI & Data) welcome the show’s first guest: Isida Drake, SVP of Security and Compliance eLearning at KnowBe4. Isida leads the global team delivering security training across 36+ languages and integrating AI directly into course development.

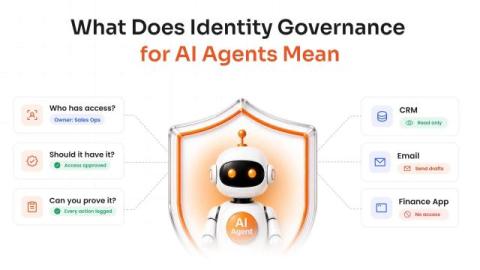
The Importance of Identity Governance for AI Agents

Identity governance answers three basic questions: Who or what has access? Should it have that access? And can you prove it later? Organizations have managed their employees this way for years. Every employee has an account, an owner, and a business reason for their access. But AI agents introduce new identities that require the same level of governance. Think about what an AI agent actually does.

Is Emergent AI Safe? Independent Pentest Findings

Is Emergent AI safe? A fair question indeed for anyone about to ship a customer-facing app from emergent.sh. Or even outside of that. Emergent is one of the fast-blooming leaders in turning plain-language prompts into full-stack web and mobile apps. What we checked is how their security holds up. Consider this a security-focused Emergent AI review. We gave four AI coding platforms the same security-explicit prompt, then attacked each app.