With enterprise digital transformations facing persistent delivery risks, experienced technical managers provide the oversight needed to avert costly delays.
With Elastic AlertZero, security teams can configure agent autonomy, audit agent activity, and choose the AI models that fit their environments without being locked into a single model provider. Mike Nichols, GM of Security at Elastic, explains how AlertZero addresses three priorities for bringing agentic AI into security operations: transparency, control, and model flexibility.
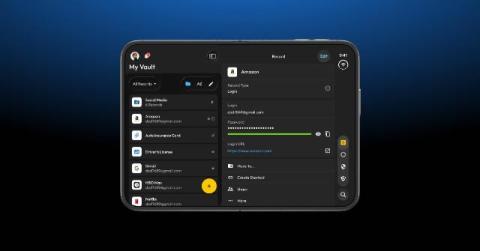
A password manager for iPhone Duo helps you store and use unique passwords without having to remember each one. Keeper Password Manager brings passwords and passkeys together in an encrypted vault, with KeeperFill to help you sign in to websites and apps. Keeper’s iOS app is designed for iPhone Duo’s displays. When the device is open, you can browse vault folders and view record details side by side. When it’s closed, the app uses the outer display.
AI hallucinations are outputs that sound accurate and authoritative but are false or invented. This Arctic Wolf video explains what AI hallucinations are, why they happen, and what they mean for cybersecurity. They happen because of incomplete data, data bias, lack of context, and processing complexity. AI predicts from patterns and doesn’t check its answers against reality. In security, the consequences include hallucinated threat assessments, incorrect remediation recommendations, fabricated indicators of compromise, wasted time, and increased risk.
Join WatchGuard’s Corey Nachreiner and Marc Laliberte for a deep dive into Shadow AI breaches from 2025 and 2026. You’ll hear about an AI coding agent that wiped a live database during a code freeze and a hiring chatbot whose admin login was 123456. Then they'll show you how to find the same risks across every client you manage with WatchGuard Cloud Detection and Response (CloudDR).
AI agents don't just answer questions anymore. They open files, use credentials, run code, install software, and run models locally, all at machine speed. Every one of those actions happens on the operating system. This is where attacks land, and where CrowdStrike Falcon Guardian excels: on the endpoint, at runtime.
AI agents are moving into production fast. They read email, call tools, query databases, and trigger business processes, often chaining those steps in ways no single team designed. Building them has never been easier. Securing what happens after an agent is manipulated is the hard part. That is the gap Salt and AWS will tackle together on Tuesday, November 10, at 9:00 am PT (12:00 pm ET) in a live session: AWS + Salt: Build Fast, Stay Secure with Agentic AI. Save your seat →
On October 19, 2026, we learned about eMudhra’s eight shockingly weak keys: where eMudhra was trusted to pick a 115-digit number for their virtual combination lock protecting the Internet, they picked the number 4. Not even four digits, just the number 4. The other seven keys were similarly weak: 56, 66, 115, 155, 156, 230 and 237. The next day, we wrote a blog post on the immediate action we took to mitigate this leak, and what customers needed to do on their end to stay secure.
In this blog, I'll explain how I found the LinkPresentation out-of-bounds write, later assigned CVE-2026-112621 and fixed in iOS 27.2 and macOS Golden Gate 27.2. LinkPresentation is the framework Apple uses to build link previews, and on an unpatched Mac, one crafted preview in Messages was enough to crash it. That fix shipped on October 26, 2026, and Apple credited me, Vinay Kumar Rasala (Xplo8E) of Appknox, alongside an anonymous researcher.
This post is based on Mackenzie's conversation with Abdel Sghiouar on The Secure Disclosure podcast. Listen to the full episode or watch below. If you give an agent the run of your cluster, it can trace a problem through every layer of the stack faster than any on-call engineer. But that same reach makes the agent worth hijacking.