Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

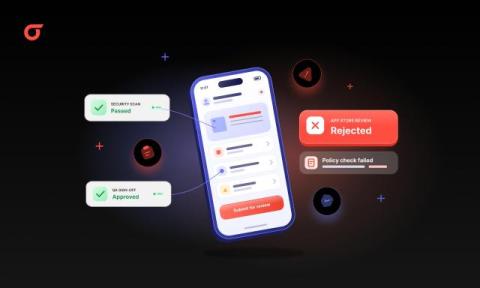
Why Your App Passes Security Testing but Gets Rejected at the Store

A security scan and an app store review ask different questions. Here's why app store rejection happens to secure builds, and what enterprise mobile teams check before they submit. Your build passed binary SAST. DAST ran clean on real devices. QA signed off, and the launch date went out to customers. Then the store console said no. Nothing in the security report was wrong. It was answering a different question.
What Makes a Good Security Agent? 5 Lessons from the AgentWorks Hackathon

Every security team is being told to adopt AI. Far fewer have been shown what "good" looks like in practice. Turnkey agents handle common, well-defined security tasks, but no two security teams operate the same way. Each has its own data, playbooks, escalation paths, and risk tolerances; unique context that no vendor can anticipate in a packaged solution.

How much AI risk is acceptable? The compromise infrastructure leaders shouldn't have to make

Spend any time with senior infrastructure and IT leaders right now and one conversation keeps coming up. The business wants AI, and increasingly it wants agentic AI: systems that don’t just recommend an action but take it. Boards have seen the productivity numbers. Competitors are announcing pilots. The pressure to move is real. At the same time, those same leaders own the risk register. They answer to regulators, auditors, and, when something goes wrong, the front page.

How Long Can a Misconfiguration Go Undetected?

Cloud applications are constantly evolving to accommodate new users, tools, and ways of working. However, every adjustment can also alter who has access to resources and what they can do with them. A misconfiguration occurs when an active setting fails to meet established security criteria. It can grant more access than necessary, keep an insecure protocol enabled, allow certain actions for too many users, or open a pathway for information to leave the organization.

Introducing HAMMER, the Homegrown Agent Maturity Model for Execution & Risk

The Homegrown Agent Maturity Model for Execution & Risk (HAMMER): is a five-level framework with seven domains for security teams to locate where they stand on securing homegrown agents, then make the case for what they need to advance. The most powerful AI agents in your enterprise may be ones you never bought. Your own teams are building them by wiring models, tools, and data into software that acts on its own, often with little security approval or oversight.

Vibe Coding Security Under Test: 100+ Vulnerabilities Across Four AI-Built Apps

Vibe-coding platforms let you go from prompt to a deployed app in a single session, a pace that outpaces the review cycles most teams built for slower releases. With Lovable nearing 8 million users by late 2025, and Replit past 50 million by April 2026, we wanted to answer a sharper question than “is vibe coding safe?” Does the platform generating the code change the outcome, and does one security prompt give you the same security everywhere?

School Event Rentals: Safety Compliance Guide for Athletic Directors

Picture a fall Friday evening: students, parents, and staff gather on the athletic field for a school carnival. As the athletic director, you're not just overseeing the scoreboard-you're responsible for ensuring every rented bounce house, obstacle course, and game booth meets safety standards. The challenge lies in balancing the festive atmosphere with strict compliance, so no one is left asking tough questions after an incident.

How Google Ads Services Are Quietly Filling Dental Appointment Books

Many dental practices do not need more website traffic. They need more booked patients. That is where Google Ads services can make a quiet but real difference. This online advertising platform puts your clinic in front of people searching right now, which is why so many practices use it to turn online interest into steady appointment demand.

Fake profile pictures: how to tell a stolen photo from an AI face

Most fake profile pictures are either a real person's photo taken without permission or a face that a generator made up. The two leave different evidence behind, so the test that exposes one will miss the other. Work out which one you might be looking at before you trust the account.