Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Model Governance: Framework, Roles, Controls and Implementation Checklist

AI models rarely become a governance problem because of the model alone. The real risk often emerges from what surrounds it: the data it receives, the decisions it influences, the systems it can access, and the people accountable for its outcomes. That makes AI model governance a lifecycle discipline, not simply a model approval process. Even NIST’s AI Risk Management Framework treats governance as a function that cuts across the entire AI lifecycle.

Prompt Injection Examples: 10 Real Attacks, and Which Ones Would Work on Your Agent

Prompt injection has not changed since 2022. What the model can do has. The instruction that hijacked a translation bot four years ago and the one that opened a homeowner’s windows last year are the same request: do something you are already allowed to do. The first system could only talk. The second could operate devices. Same sentence, different consequence. Here are ten real attacks, in order, and for each one the thing the system was allowed to do that made it work.

What Is Prompt Injection, Really? Why the Textbook Answer Cannot Tell You If You Have an Incident

Prompt injection is three things happening at once. The definition written in 2022 described a model that followed an instruction hidden in the text it was asked to translate. The definition needed in 2026 describes an agent that read a support ticket and then queried a customer table it had never touched, using a service account nobody had revoked. Those are the same attack.

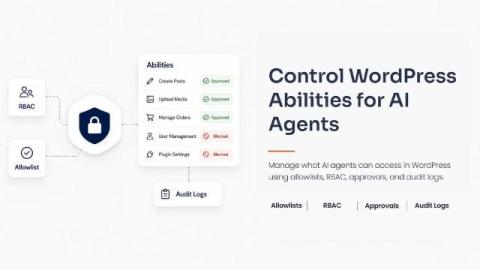
How To Control Which WordPress Abilities an MCP Client/AI Agent Can Use

Connecting ChatGPT, Claude, or another AI agent to WordPress can turn simple instructions into real website actions. An agent can create posts, update pages, upload media, manage orders, and handle other tasks when the right MCP tools are available. The interesting part starts when you decide how much access to give it. A content management agent may need posts and media, while a WooCommerce support agent may need orders and customer information.

The Truth About Insider Threats: AI, Paranoia & Hybrid Work | MSP Series

Every organization thinks insider threat is someone else's problem — until it isn't. Join host Alex Courson as she sits down with two leading experts who have spent their careers on the front lines of insider risk: Shawnee Delaney (former CIA-trained DIA case officer and CEO of Vaillance Group) and Peter Hadjigeorgiou (Field CISO at Teramind). Whether you run a business, work in IT, or manage people in a remote, hybrid, or in-office environment, this conversation is for you. We dive deep into AI in the workplace, workplace paranoia, and how organizations need to evolve to drive real change.


Hot Take: Over-permissioned agents will be the next big breach.

The next big breach won't be a hacker. It'll be an over-permissioned agent. Someone approved an agent action at some point, for a reason that made sense at the time. But access persisted long after a task was performed. Stale permissions without human intervention could turn into exposure. Listen to perspectives from people who see this problem from different roles.

Introducing Adaptive Intelligence: Undermining the economics of every bot attack

Modern bot threats are increasingly driven by determined, sophisticated attackers. Often it is not even one person, but a group trading techniques with each other or a commercial service sold to anyone willing to pay. For many of them, getting past bot detection is a full-time job they genuinely enjoy. Block them and they get to work, finding a workaround. AI has simplified this further, making it even easier to set up complex configurations for attackers, lowering the overhead of an attack.

How Zenity Implements the 2026 OWASP Top 10 for LLM Applications

Ask AI to Choose a prompt Write a TLDR of this post Explain the security risk Summarize what CISOs should know Every AI security framework names the risks you have to control. Zenity is built to implement those controls at runtime. Here's the 2026 OWASP Top 10 for LLM Applications, entry by entry, with the gaps marked honestly. Paste a booby-trapped instruction into a chat window, and nothing much happens.