Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

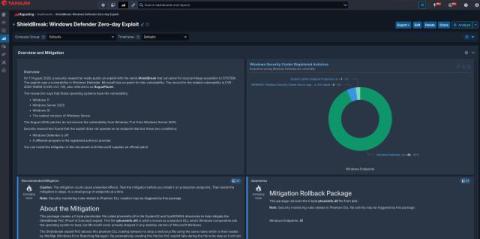
ShieldBreak: The Windows Defender 0-Day with No Patch - And What to Do About It.

In mid-June 2026, Microsoft acknowledged RoguePlanet, a privilege-escalation flaw in the Microsoft Malware Protection Engine (mpengine.dll), the scanning engine behind Windows Defender. Microsoft rated it "Exploitation More Likely" on its Exploitability Index and assigned a CVSS score of 7.8. Microsoft shipped a fix in Malware Protection Engine version 1.1.26060.3008 during its July 2026 patch cycle.
5 Things to Consider Before Using SSVC to Automate Vulnerability Prioritization

Security teams can’t remediate every vulnerability the moment it appears, so prioritization must separate urgent, business-critical risks from noise. This is complicated by the fact that traditional scoring methods like CVSS often lack the context needed to decide what should be fixed first. The Stakeholder-Specific Vulnerability Categorization (SSVC) framework is one option many organizations use to fill this gap as part of automating vulnerability prioritization.

Emerging Threat: (CVE-2026-26035) FortiWeb Admin Authentication Bypass via RADIUS Admin Groups

CVE-2026-26035 is an improper authentication vulnerability (CWE-287) in Fortinet FortiWeb, disclosed by Fortinet on August 12, 2026 in advisory FG-IR-26-158 under the title “Broken access control in the RADIUS type admin group.” The flaw sits in FortiWeb’s remote RADIUS administrator authentication path, where the appliance fails to correctly validate an administrative login before granting access.

Emerging Threat: (CVE-2026-72766) n8n Arbitrary File Read and SSRF via Send Email Node

CVE-2026-72766 is a type confusion vulnerability in the Send Email node of n8n, an open-source workflow automation platform. The node does not enforce that its message fields hold string values, so a non-string value arriving from a workflow expression can be passed through to the underlying mail library, Nodemailer, which interprets it as a file path or a URL rather than message text. The vulnerability carries a CVSS v3.1 base score of 7.5 (High). Under CVSS v4.0 it scores 8.2 (High).

Emerging Threat: (CVE-2026-20349) Cisco ASA and FTD Denial of Service via Remote Access SSL VPN

CVE-2026-20349 is a denial of service vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software and Cisco Secure Firewall Threat Defense (FTD) Software. The flaw stems from insufficient error checking when the service processes HTTP requests. The vulnerability carries a CVSS v3.1 base score of 8.6 (High). Cisco tracks it under CWE-244.

AI Can't Do CTEM Alone (And Neither Can You)

AI can meaningfully power Continuous Threat Exposure Management (CTEM), but only for specific stages of the cycle: prioritization, validation, and remediation routing. AI can’t replace the underlying data integration work, and it can’t turn CTEM into a single product, because Gartner defines CTEM as a continuous five-stage program (scoping, discovery, prioritization, validation, mobilization), not a tool you install.

Microsoft Defender Patch Bypass: High Severity Zero-Day Privilege Escalation (CVE-2026-50656/RoguePlanet, ShieldBreak)

A critical zero-day vulnerability (CVE-2026-50656/“RoguePlanet”) in Microsoft Defender’s Malware Protection Engine (mpengine.dll) enables local users, including standard, low-privilege accounts, to escalate privileges to NT AUTHORITY\SYSTEM using a race condition and improper link resolution. Microsoft initially issued a patch (Engine v1.1.26060.3008) in July 2026.

The Agent Baseline: 35 controls, but where should you start?

Two weeks ago, we published the Agent Baseline alongside Docker and Keycard. In it, we describe six security outcomes, 35 controls, and an open reference architecture for running AI agents at the enterprise level. Last week, we stress-tested it: we took it to a panel at Black Hat and spent about one hour being asked hard questions about it. Play Video: Snyk x Docker x Keycard | Agent Baseline Panel @ Black Hat 2026 The most useful question came from someone who had actually already read it.

Emerging Threat: (CVE-2026-34265) SAP NetWeaver ABAP Memory Corruption via DIAG Protocol Parsing

CVE-2026-34265 is a memory corruption vulnerability in the Application Server ABAP component of SAP NetWeaver and the ABAP Platform. The flaw stems from logical errors in how the SAP kernel parses DIAG protocol messages, the proprietary protocol that carries traffic between the SAP GUI presentation layer and the application server. Malformed input reaching the parser leads to an out-of-bounds write, classified as CWE-787. The vulnerability carries a CVSS v3.1 base score of 9.8 (Critical).