Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Emerging Threat: (CVE-2026-21580) Confluence Privilege Escalation via Unauthenticated Stored XSS

CVE-2026-21580 is a stored cross-site scripting vulnerability in Atlassian Confluence Data Center and Server, which the vendor advisory groups together with a privilege escalation component and a security misconfiguration weakness. An attacker persists crafted HTML or JavaScript on a vulnerable instance, and that payload executes later in the browser of whichever user views the affected content. The vulnerability carries a CVSS 4.0 base score of 8.6.
How to Develop Vulnerability Assessment Skills Through Cybersecurity Courses

This process is a vital part of digital protection because it helps organizations identify technical flaws before unauthorized users exploit them. Experts who develop accurate evaluation skills examine computers, networks, software and settings to determine where security upgrades are required. Cybersecurity courses offer structured information plus hands-on practice to help students learn evaluation methods, analyze results and suggest specific safety protocols.

We Solved Visibility. Now We Have to Solve the Work

Consolidating every security finding into one place solves visibility, but it doesn’t reduce risk on its own. Aggregation without context just makes the backlog feel bigger. Real remediation depends on answering four questions about each exposure: what needs fixing, why it matters, where the fix happens, and who owns it.

When Reading Apps Handle Sensitive Documents: A Practical Privacy Checklist

Read-aloud and AI explanation tools can make difficult material easier to use. Before opening a confidential PDF, however, users should understand where the text goes, what the app stores and which permissions it really needs.

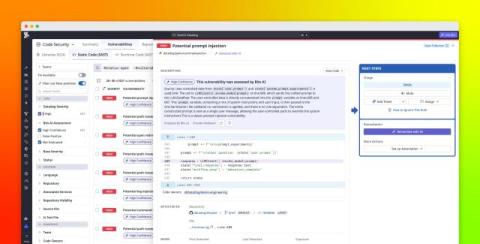
Detect vulnerabilities in LLM applications with Datadog's AI-native SAST

AI coding tools help developers build and deploy LLM applications quickly, but this speed comes with new security risks. Traditional static application security testing (SAST) tools that are pattern based weren’t designed to detect LLM-specific issues such as prompt injection sinks and exposed system prompts. These vulnerabilities often don’t become apparent until applications are already running in production, when remediation is more difficult and expensive.

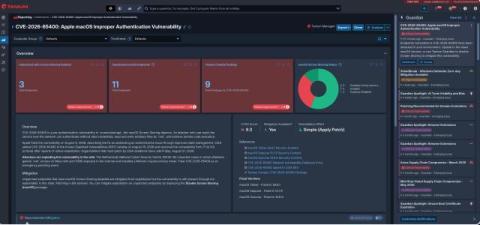
Critical macOS Screen Sharing Authentication Bypass - Under Active Exploitation (CVE-2026-65400)

On August 6, 2026, Apple shipped an emergency, out-of-band fix for CVE-2026-65400, an authentication issue in screensharingd, the daemon behind Screen Sharing, macOS's built-in remote desktop service that listens on TCP port 5900. Apple's advisory describes an attacker who could reach the service over the network and authenticate without valid credentials, then read and write files as root—enough to achieve full remote code execution.