Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What Are Moltbot and Moltbook? Why the Agentic AI Frenzy Is a Security Trap

AI agents aren’t taking over. But agentic AI without security is a real problem. Over the last few days, Moltbot and its social platform Moltbook have surged across headlines and social media. Some are calling it a glimpse of artificial general intelligence. Others say AI agents are organizing themselves. That’s not what’s happening. In this video, SecurityScorecard’s Jeremy Turner, VP of Threat Intelligence & Research, breaks down what Moltbot actually is, why this isn’t AGI, and where the real danger lives.
ChatGPT Oopsies Series of Information - The 443 Podcast - Episode 356

This week on the podcast, we cover a Politico report detailing a security lapse at CISA in the United States involving sensitive data and a public version of ChatGPT. Next, we dive into a couple of recently resolved vulnerabilities in the SolarWinds Web Help Desk application. Finally, we end with some closure on a story about two Coalfire penetration testers who were arrested several years ago for completing a penetration test in Iowa.

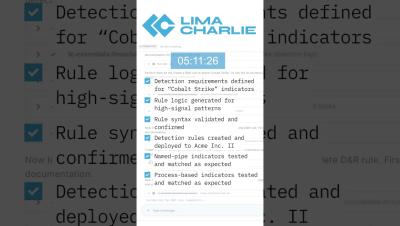
Claude Code writes and tests Cobalt Strike detection rules #cybersecurity #ai #securityoperations

Watch Claude Code generate production-ready Cobalt Strike detection rules in LimaCharlie. The agent defines detection requirements, creates rule logic for high-signal patterns, validates syntax, and deploys rules to the tenant. Named-pipe indicators and process-based signatures are tested against positive and negative controls to confirm accuracy. Security teams can operationalize threat-specific detections in minutes instead of hours.

5 Essential AI Tools for Project Managers to Boost Productivity in 2026

It's 2026, and if you're still manually color-coding spreadsheets or manually typing meeting minutes, you're stuck in the past. We are no longer "task trackers", we're "strategic navigators". But with the release of GPT-5.2 and the deluge of AI agents, it's noisy. I've seen so many PMs download 20 different AI apps and they're all the same: "generating some generic text for you". If you really want to save time, you don't need more writing tools; you need a varied toolkit that takes care of the different parts of your brain: your scheduler, your communicator, your designer, your librarian.

Claude Code builds security infrastructure with Git-based configs #cybersecurity #ai #secops

See Claude Code provision a new LimaCharlie security tenant with regional data residency, enable detection extensions, generate API credentials, create SSH keys, and establish Git as the single source of truth. Security teams can manage their entire LimaCharlie detection infrastructure through version-controlled code rather than point-and-click interfaces.

Giving OpenClaw The Keys to Your Kingdom? Read This First

In security, we never assume perfection. We assume zero-trust, and we design controls to limit the blast radius. That mindset is missing from many OpenClaw deployments today. It is almost impossible not to hear about the new personal AI assistant, OpenClaw (formerly known as ClawdBot and MoltBot). Since its release in November 2025, it has taken the tech world by storm, rapidly accumulating well over 100,000 stars, tens of thousands of forks, and millions of visitors.

Secure AI with CrowdStrike: Real-World Stories of Protecting AI Workloads and Data

AI is reshaping business at machine speed. From automating claims to improving customer engagement, organizations are embedding AI into core workflows faster than most security teams can track. As AI systems expand, they introduce a new class of security considerations. AI no longer lives in a single layer of the stack. It runs on cloud infrastructure, processes sensitive data, and operates through a growing network of human and non-human identities.

Snyk Advisor is Reshaping Package Intelligence on Snyk Security Database

Choosing safe, healthy open source dependencies shouldn’t require jumping between tools or piecing together context from multiple places. Developers and AppSec teams need package health signals exactly where security decisions already happen. This is why we’re bringing Snyk Advisor data into security.snyk.io.

The CISA ChatGPT Incident Makes the Case for AI-Native DLP

The acting director of America's Cybersecurity and Infrastructure Security Agency—the person tasked with defending federal networks against nation-state adversaries—triggered multiple automated security warnings by uploading sensitive government documents to ChatGPT. If this happened at CISA, it can happen at your organization too.

API-Based Zero Trust Assessment: Measuring Your Security Posture in Minutes

Zero Trust (and probably many general posture) conversations stall at one question: Where are we actually today? Because Reach connects directly through APIs, teams can quickly assess their environment without deploying new agents or ripping anything out. That makes it practical to benchmark a Zero Trust program against the CISA Zero Trust Maturity Model — and see what’s real vs. assumed.