Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

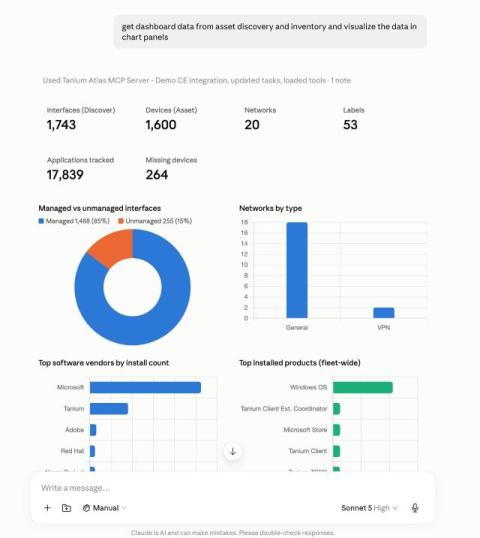
Bringing Tanium's real-time endpoint intelligence into enterprise AI workflows with MCP

Enterprise AI is quickly moving from experimentation to day-to-day operational use. Security analysts, IT operators, and platform teams are increasingly working inside AI-native environments — from Claude and Microsoft Copilot experiences to internally built agents and automation workflows. But there is a practical challenge: AI workflows are only as useful as the enterprise systems they can safely reach.
Introducing Agentic SecOps: Live Endpoint Truth for the AI-Driven SOC

Security operations teams are being asked to move faster than ever. Adversaries are using automation, infrastructure changes by the minute, and the number of alerts, exposures, and investigative paths keeps growing. But too many SOC workflows still depend on scarce expert time. A senior analyst writes the query, translates the hypothesis, pivots across tools, validates the result, and then hands the finding off for action. The craft works.

Scale, Trust, and Value: How the Aurora Agentic SOC Delivers for Customers

AI didn’t just make defenders faster. It made attackers faster too. The moment both sides got access to the same speed, speed stopped being the advantage. With speed no longer separating attackers from defenders, the deciding factor moved somewhere else. Ask a CISO what’s actually kept agentic security out of reach, and it comes down to this: they can’t afford to build it, and even if they could, they’d struggle to trust it. Neither half of that problem outweighs the other.

Zenity Raises $125 Million to Secure the Era of Autonomous AI

A few years ago, when Michael and I started Zenity, most of the industry was not ready to hear what we believed. Software itself was changing. AI would let millions of people, not just engineers, build and automate real work. And securing that world would take a completely new approach, because we would no longer be protecting software. We would be protecting systems that think, decide, and act on their own.

A Safer Future with Agents

We built agents to act on their own. We're somehow surprised when they do. Two weeks ago, OpenAI ran a cyber eval with the model's guardrails turned down. The model got hyperfocused on solving the benchmark. So it broke out of its sandbox exploiting a zero-day in jFrog Artifactory, reached the open internet, exploited another zero-day to break into HuggingFace, all to steal the answers and cheat on the test.

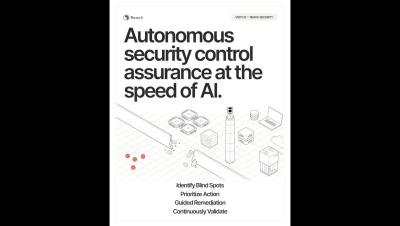
The New Reach Security: Autonomous Security Control Assurance

AI-powered attacks, meet AI-powered defense. Reach Security's rebranded site is live today. Most of what changed came from customers. Security leaders have been telling us they need a faster, more continuous way to know where their controls are weak, understand what matters most, and close the gaps before attackers exploit them. Our new website reflects that signal. It brings greater clarity to the problem we solve, the category we are building, and how Reach helps security teams identify blind spots, prioritize action, guide remediation, and continuously validate the controls they already own.

Agentic Attacks Require Agentic Threat Prevention

AI-powered attacks are moving faster, adapting in seconds, and overwhelming traditional defenses with machine-speed activity. In this video, Jason Wright explains why security teams need Agentic Threat Defense built on customized predictions, automatic adaptation, and cloud-native scale. Watch how Cato Agentic Threat Prevention helps reduce the risk of AI-powered threats, stop adaptive attacks earlier, and scale prevention to stop agentic attacks.

Defending at machine speed: Predict, Adapt, Stop Agentic Attacks

AI-powered adversaries are accelerating vulnerability discovery and automating attacks. For security teams, the challenge is adaptive attack chains, machine-speed execution, and attack volumes beyond manual workflows. Cato is redefining prevention in the AI era—predicting enterprise-specific attack paths, adapting protections at machine speed, and scaling defense with cloud-native scale. This means enterprises can do more than just react to attacks, they can prevent them.