Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Superior Long-Term Investment for Municipal Planners: Solar Street Lights or Traditional Systems?

Smart, green infrastructure is becoming the norm for municipalities across the globe, and public lighting is one of its critical components. Solar street light systems are becoming increasingly popular as a cost-effective and sustainable solution compared to traditional street lighting systems. For municipal planners, the decision of choosing between both technologies is extremely important in terms of long-term returns on investments.
DORA Non-Compliance Could Cost Your Business

Prompted by a new era of cyber-attacks surging downtime and data breaches, the Digital Operational Resilience Act (DORA) regulation came into force on 17th of January to reshape how organisations approach security, privacy and cybersecurity. Cybercriminals are becoming increasingly daring and creative, with an expected rise in the exploitation of new vulnerabilities in 2025.

Cybersecurity Compliance in Finance: Why It's Your First Line of Trust, Not Just a Checkbox

In financial services, trust is everything. Clients trust you with their data, their money, and their future. But that trust can vanish overnight—especially when a cybersecurity incident exposes weak governance or regulatory non-compliance. In today’s threat landscape, financial institutions are more than just attractive targets for cybercriminals—they’re often the most regulated, most scrutinized, and most unforgiving places for a security slip.

A 7-step Essential Eight compliance checklist

Implementing Essential Eight (E8) is mandatory for in-scope organisations, such as government agencies, critical infrastructure providers, and other non-corporate Commonwealth entities (NCEs). ‍ Even if your organisation isn’t scoped by the framework, aligning with E8 is recommended because it outlines the baseline requirements for defending against cyber threats.

Introducing Vanta Trust Maturity Report: Benchmark your security maturity against 11,000+ programs

Security is no longer just part of running a business—it’s the backbone of building customer trust. But there’s no one-size-fits-all approach to building a reliable and scalable security program. Every organization—regardless of size, industry, or region—faces unique challenges that shape its security needs and investments. ‍ Customers often tell us they want more tools to benchmark their programs against industry peers and best practices.

Vanta is a Leader in the IDC MarketScape: Worldwide Governance, Risk, and Compliance Software Vendor Assessment, 2025

Vanta's AI-powered trust management platform centralizes key program areas, reduces manual efforts with automation, and continuously monitors your GRC program to drive measurable business impact. Recently, Vanta was named a Leader in the IDC MarketScape: Worldwide Governance, Risk, and Compliance Software Vendor Assessment 2025 (Doc # US53615325, June 2025). ‍ The IDC MarketScape assesses the competitive landscape, analyzing qualitative and quantitative criteria to evaluate GRC vendors.

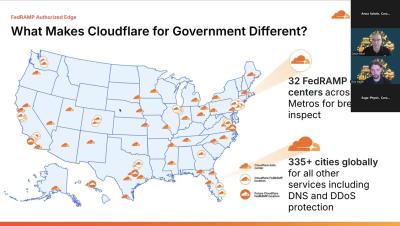
Data Control at the Edge Cloudflare & FedRAMP in Action

This exclusive webinar discovers how Cloudflare helps agencies stay secure and compliant. Cloudflare Data Localization Suite allows customers to leverage the resiliency, security and performance of the Cloudflare global anycast network while maintaining appropriate data residency controls. This session explores Cloudflare’s unique approach to FedRAMP compliance. Learn how FedRAMP authorized services from Cloudflare can help agencies and contractors enhance, secure and monitor both public and private applications whether hosted on-prem or in the cloud.

How to get HITRUST certified

How to get HITRUST certified has become a strategic move for organizations handling sensitive health and financial data. It demonstrates a serious commitment to information security, privacy, and regulatory compliance. However, the path to certification is often viewed as daunting – requiring time, budget, internal effort, and cross-functional coordination. Many organizations struggle with cost concerns, internal resource limitations, and uncertainty about the actual return on investment.

SOC 2 complete guide

SOC 2 compliance is no longer a “nice to have” – it’s an essential requirement for SaaS providers and service organizations handling sensitive client data. Whether you’re a startup looking to build credibility or an established firm entering enterprise deals, SOC 2 offers a structured framework to demonstrate your commitment to security, privacy, and operational integrity.