Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

When Geopolitics Hits Your Balance Sheet: What Binance's $6.3B Hack Means for CTOs

Binance never chose to be on the front line of a geopolitical conflict, yet if blockchain-intelligence firms are right, that is where it ended up, and its balance sheet absorbed the first loss. Binance’s initial investigation indicates that a compromised DevOps engineer’s laptop may have given an attacker access to a service container and the ability to submit unauthorised withdrawals.
PCI Compliance Logging: Complete Guide to Requirement 10

Of the 12 Payment Card Industry Data Security Standard (PCI DSS) requirements, Requirement 10 is one your platform team can engineer directly. Under the PCI DSS v4.0.1 standard, automated log review has been a tested requirement since March 31, 2025. Your assessor will test the mechanism that performs the review. This PCI compliance logging guide covers each 10.x sub-requirement, maps the seven event classes to log sources, and lays out a nine-step program you can hand to your assessor.

Fake profile pictures: how to tell a stolen photo from an AI face

Most fake profile pictures are either a real person's photo taken without permission or a face that a generator made up. The two leave different evidence behind, so the test that exposes one will miss the other. Work out which one you might be looking at before you trust the account.

How Arrests Without a Conviction Affect Employment and Background Checks

An arrest that never leads to a conviction can still surface on a background check. Whether you can see that record-or use it-rests on strict reporting rules and anti-bias limits. On October 29, 2026, the EEOC scrapped its decade-old guidance, leaving many online explainers out of date. This guide answers four rapid-fire questions-Does the record exist? Can a vendor report it? May you weigh it? What guardrails apply?-so you keep talent moving and systems secure while staying inside the new legal lines.

CVE-2026-97229: GitLab RCE Added to CISA KEV

October 2026 has been an unusually loud month for critical disclosures across the ecosystem. Along with PHP2Shell, GitLab also joined the party and shipped three critical RCEs in the same month: CVE-2026-90970 (CVSS 9.9) in the self-hosted AI Gateway on October 2, then CVE-2026-97229 (CVSS 10.0) on October 12, and CVE-2026-110264 (CVSS 10.0) on October 21. The last two are integer overflow bugs in the exact same regex compiler, shipped nine days apart.

Manage Passwords on iPhone Duo With Keeper

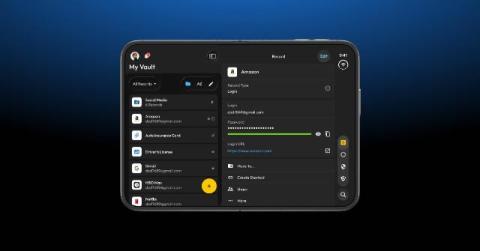
A password manager for iPhone Duo helps you store and use unique passwords without having to remember each one. Keeper Password Manager brings passwords and passkeys together in an encrypted vault, with KeeperFill to help you sign in to websites and apps. Keeper’s iOS app is designed for iPhone Duo’s displays. When the device is open, you can browse vault folders and view record details side by side. When it’s closed, the app uses the outer display.

CrowdStrike Expands Falcon Adversary OverWatch Threat Hunting Across AI and Google Cloud

As adversaries broaden their operations across cloud environments, identities, SaaS applications, and AI systems, security teams need threat hunting that can keep up. Suspicious activity in one environment may be part of a larger intrusion spanning multiple domains, making it increasingly important to connect signals across the attack surface. To expand detection coverage across the widening attack surface, CrowdStrike Falcon Adversary OverWatch threat hunting has added two key capabilities.

Build an Intelligence Advantage with Falcon Next-Gen SIEM

Every organization has a different threat profile. Industry, geography, infrastructure, business operations, and the broader technology ecosystem all influence which adversaries and threats matter most. The challenge is putting threat intelligence to work at scale to identify the greatest threats to each business. The intelligence that security teams rely on is as varied as the threats they face.

CrowdStrike Agent Graph Shows How Agents Act on the Endpoint

AI agents don't just answer questions anymore. They open files, use credentials, run code, install software, and run models locally, all at machine speed. Every one of those actions happens on the operating system. This is where attacks land, and where CrowdStrike Falcon Guardian excels: on the endpoint, at runtime.