Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why Modern Email Security Requires More Than Sender Reputation

For years, email filtering worked from a stable premise: malicious messages would expose themselves through something observable. A suspicious domain, a spoofed sender, a known-bad attachment or a URL with poor reputation gave defenders a concrete signal to block. Those controls still stop commodity phishing. What has changed is that many convincing attacks now inherit trust rather than imitate it.
What Is CAC Authentication? A Complete Guide to Common Access Card Authentication

CISA calls phishing-resistant MFA the standard every organization should be working toward. For DoD components, federal agencies, defense contractors, and other organizations operating at NIST's highest authenticator assurance level (AAL3), that guidance narrows to two paths: FIDO2/WebAuthn, or PKI-based smart cards like CAC and PIV.

Modern Treasury is powering $400B+ in global payments - S3E14

In this episode, we're excited to introduce Matt Marcus, Co-Founder and CEO of Modern Treasury, the most trusted infrastructure for global money movement. Founded in 2018 alongside co-founders Dimitri Dadiomov and Sam Aarons through Y Combinator's Summer 2018 batch, Modern Treasury has powered over $400 billion in payments for hundreds of organizations, ranging from YC startups to financial institutions with over a century of history.

HR Onboarding Automation with Identity Governance, Auditing, Access Control via JSM

In this video, we demonstrate how to automate the HR onboarding process using the Identity Governance, Auditing & Access Control via JSM app. You'll learn how to create an onboarding automation workflow that provisions new employees, assigns applications and roles, routes approvals, and tracks every action with complete audit visibility, all from within Jira Service Management. In this video, you’ll learn how to.

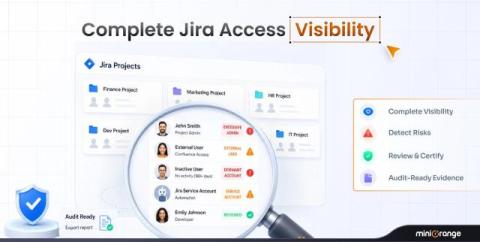
Jira Access Reviews: How to See Who Has Access to Every Project, Before an Auditor Asks

If you’ve managed Jira for a while, you've probably seen permissions grow more complex over time. You might have accounts that were granted temporary access during a migration but are still retaining it today. Or maybe contractors whose access was never revoked. You can clean that up. But with hundreds of users and projects, it’s going to take forever. Things become even more complicated when you're preparing for a SOC 2, ISO 27001, or SOX access review.

How to Connect Claude to Jira Securely Without Giving AI Unrestricted Access

Teams are connecting Claude to Jira to summarize issues, draft tickets, and answer sprint questions in seconds. The productivity gains are real, but so is the security risk. The problem is simple: a direct connection gives Claude the same permissions as the person who set it up. If that user can view confidential projects or delete issues, so can Claude. There's no business logic in between deciding what AI should and shouldn't touch. Most organizations don't want to ban AI.

Webinar Recording: AI Governance & Policy Enforcement for the Abilities API

In this Webinar, Learn to secure your WordPress AI agents against common risks. Understand how to implement audit trails and smarter permissions for your site. Integrating AI agents with WordPress offers powerful marketing capabilities, but it introduces significant security vulnerabilities. This webinar explains how to manage these risks by addressing scoping, identity verification, and access control. If you are a developer or site owner building autonomous workflows, this breakdown highlights exactly where your current setup might be exposed.

The Identity Surface You're Not Watching: Three Layers of Coding Agent Risk

There's a widespread assumption in enterprise security that identity is a problem IAM programs know how to solve. Provision the right access, enforce least privilege, audit the credential chain, and you've addressed the identity risk. For human users and traditional service accounts, that's approximately correct. For coding agents, it misses two-thirds of the problem. Coding agents don't have a single identity. They operate across a layered identity surface, and each layer carries its own risk profile.

Smart Card Authentication: A Complete Guide To Secure Enterprise Access

If you're evaluating multi-factor authentication for a bank, a hospital network, a defense contractor, or a government agency, you've probably already run into smart card authentication. It's the method behind the CAC (Common Access Card) and PIV (Personal Identity Verification) cards federal employees badge in with every day. It's also becoming the default authentication method that regulated industries reach for, once passwords and OTP codes stop being good enough.

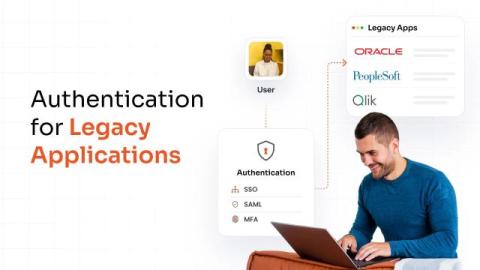
Modern Authentication for Legacy Applications Explained

Your ERP system doesn't know what a SAML assertion is. Neither does that 15-year-old internal tool running your warehouse floor. But your identity team just rolled out Microsoft Entra ID with conditional access, MFA, and zero trust policies everywhere. That gap is what modern authentication for legacy applications closes.