Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Your Vulnerability Backlog Is No Longer Technical Debt, It's an Attack Surface

Every security program has one: a queue of a few thousand findings, or a few hundred thousand, that nobody has worked through and nobody expects to. Most teams file it under technical debt, a cost carried on purpose, paid down when there is room, and tolerable because the interest rate stays low. That accounting held for a long time, because it rested on a single assumption: almost nothing in the queue would ever be reached, or exploited, by anyone.
Why Carbon Data Needs the Same Controls as Financial Records

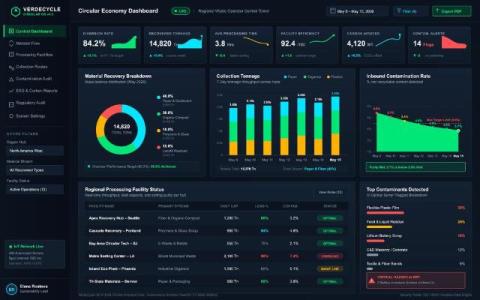
Most security teams know exactly where their financial records live, who can edit them and how every change gets logged. Ask the same questions about the company's emissions data and the answers often get vague. That gap matters more each year. Greenhouse gas figures now end up in regulatory filings, investor reports and assurance reviews, which means they carry the same risks as any other disclosed number.

A UX Firm in Delaware and Designing for Fintech: Two Different Briefs

The short version Two searches show up in the same procurement folder. One looks for a UX firm Delaware founders can meet without a flight. The other looks for a team that has already shipped a regulated financial product. Those searches answer different questions, and the second one is harder to fake.

Emerging Threat: (CVE-2026-94545) Next.js Remote Code Execution via ImageResponse SVG Injection

CVE-2026-94545 is a remote code execution vulnerability in the next/og ImageResponse API of Next.js, the React framework maintained by Vercel. ImageResponse generates images on the server, typically Open Graph preview cards, by rendering markup through the Satori library into SVG and then into a raster image.

Provider to Advisor: The MSP Shift Toward Risk Leadership | WatchGuard Webinar

Most MSP client reviews cover what got installed. The endpoint agent was deployed, the firewall rules were tuned, and the tickets were closed inside the SLA. Meanwhile, boards, insurers, and auditors are asking for something more: a clear account of the business's current security and compliance risks. The partner who can provide that answer earns client trust and increases credibility.

Modern Data Security Should Be Anchored To Your Data's Lineage

New AI tools appear every day. The novelty and utility they bring, along with the constant pressure to be more productive, pull employees toward them to get work done faster. The intent is good but the effect can range from problematic to damaging, because while there are rules in place for sanctioned tools, there are none for the ones that quietly show up in between.

iGaming Fraud Prevention: How to Protect Player Accounts Preemptively Without Adding Friction

iGaming fraud prevention does not have to mean applying more security checks broadly across the player journey. For player account takeover, the better objective is to obtain enough reliable risk context early enough to reserve additional checks for the accounts and access attempts that actually warrant them. The commercial stakes are growing alongside the market. U.S. iGaming revenue reached $10.73 billion in 2025, up 27.6% year over year, according to the American Gaming Association.

The Great Infrastructure Reset: Infrastructure Conversations Have Changed

Infrastructure conversations have changed. Today, customers are balancing rising infrastructure costs, licensing renewals, and the need for greater cyber resilience all at the same time. We’re calling this The Great Infrastructure Reset: a shift in infrastructure strategy driven by market forces that customers can’t ignore. For our partners, this creates an opportunity to lead with strategic conversations. Help customers understand what’s changing, what it means for their business, and how to build an infrastructure strategy for what’s next.

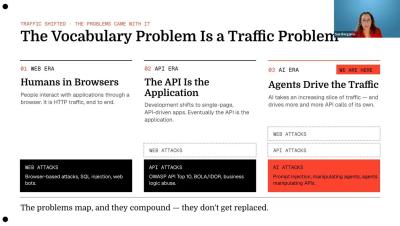
WAF vs WAAP API vs AI What Security Tools Do You Actually Need?

A straightforward framework for matching each layer of protection to the problem it actually solves. Trying to understand vendors in the modern application security space can feel a lot like trying to solve word scramble. Whether it’s remembering what the “A’s” in "WAAP” stand for, figuring out if “WAF” includes APIs, or assessing the actual function of a new AI security product, understanding what tools your team actually needs is getting harder all the time.