Security teams aren’t ready for autonomous agents that trigger real-world actions. These aren’t just chatbots—they’re systems with access to your APIs and infrastructure.
Mend.io, formerly known as Whitesource, has over a decade of experience helping global organizations build world-class AppSec programs that reduce risk and accelerate development -– using tools built into the technologies that software and security teams already love. Our automated technology protects organizations from supply chain and malicious package attacks, vulnerabilities in open source and custom code, and open-source license risks.
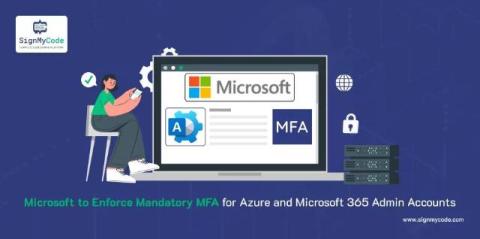
Microsoft has also been enhancing cloud security by ensuring that multi-factor authentication (MFA) is enabled for all of its Azure and Microsoft 365 administrative accounts. The rollout will begin with Azure portals in October 2025 and progressively to command-line tools, APIs, and Infrastructure-as-Code (IaC) environments in October of that year. For organizations, it means adapting their authentication workflows to align with Microsoft’s phased enforcement plan or risk disruption.
At the RSAC Conference this year, it seemed that every cybersecurity company had suddenly become an agentic AI company. According to such vendors, AI agents were the solution to every security problem keeping CISOs up at night. The audience, however, was understandably skeptical. Concerns over vendor promises fell into two camps. The first camp: companies that took whatever AI capabilities they had and slapped the word ‘agentic’ on them (aka ‘agent-washing’). Or even worse.
In our last post, we introduced the Model Context Protocol (MCP), the "brain" or "mission briefing" that guides an AI agent's actions. Most security teams are just getting familiar with prompt injection, the equivalent of tricking an AI with a single, misleading command. But that's like stopping a pickpocket at the door when a master spy is already inside, rewriting the mission plans. As AI agents become autonomous, the attacks become more profound.
Remember when we thought the application layer was where all the fun happened? Firewalls, WAFs, EDR, dashboards galore — the entire security industrial complex built around watching what apps do. Well, with “agentic AI” running the show, that middle ground is turning into a bypass lane. Instead of clicking through UIs or APIs, your AI buddy is making direct system calls, automating workflows at the OS and hardware level.
2025 is the year privacy becomes the competitive layer of AI. If you’re rolling out GenAI privacy is no longer a compliance chore; it’s a trust-building strategy that accelerates adoption, partnerships, and revenue. This report distills the most important AI privacy issues, statistics, and trends shaping 2025: what they mean, and how to respond with practical guardrails that protect people and performance.
AI marketing platforms have exploded in popularity, becoming everyday tools for creative teams in enterprises worldwide. Platforms like Simplified AI offer marketers the ability to generate content, clips, and campaigns at scale. For CISOs and IT leaders, approving such services often seems straightforward: allow access, whitelist the domain, and enable the marketing team to innovate.
As the summer winds down and conversation around AI Security heats up, the Snyk team is in full swing planning mode for a double-header this October—with the return of DevSecCon’s Flagship conference, focusing this year on Securing the Shift to AI Native, and serving as the founding partner of the inaugural AI Security Summit.
AI agents are rapidly evolving from simple text generators into powerful autonomous assistants that can browse the web, book travel, and extract complex data on our behalf. This new “agentic” AI, which operates in a “sense-plan-act” loop, promises to revolutionize how we interact with the digital world.