Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What you need to know about the new 2023 OWASP API Security Top 10

The 2023 OWASP API Security Top 10 list compiles and explains the most recent and pressing security threats facing today’s complex API ecosystem. As part of the committee that defined this industry-framing list, Salt gives you an insider view into the categories and how those embarking on their API security journey can most effectively address the critical vulnerabilities raised.
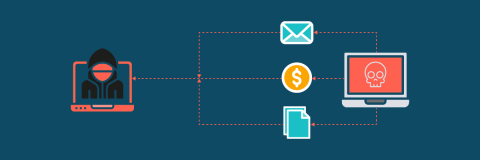
CVE-2023-34362 - Zero-Day Vulnerability Discovered in MOVEit Transfer is Exploited in the Wild by Cl0p Ransomeware - Here's What you Need to Know

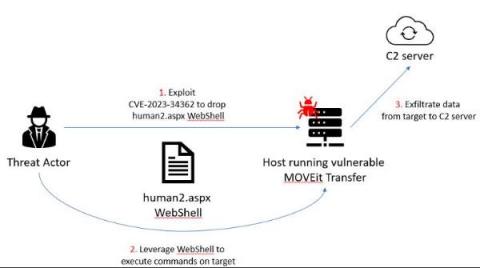
On May 29, 2023, a critical security vulnerability, identified as CVE-2023-34362, was published, leaving users of MOVEit Transfer software at high risk. According to Progress, organizations have reported possible exploitation in the wild. Therefore it’s crucial that any business using MOVEit Transfer to take immediate action, especially since all versions of this popular file transfer software are affected by this vulnerability.

Minimizing Intrusion Detection Time with Cyber Threat Intelligence

With the increasing frequency of cyber-attacks, businesses need to prioritize proactive early incident detection. In this blog, we will highlight the significance of a high-quality threat intelligence solution in building a well-rounded and proactive defense strategy. In an era defined by pervasive connectivity, businesses of all sizes find themselves grappling with an escalating threat of cyber-attacks.

BestinBAS Threat Researchers Discover Their 40th CVE

SafeBreach Labs is the research and development arm of SafeBreach. SafeBreach Labs delivers cutting-edge vulnerability and cybersecurity research as well as novel product ideas. Real-world insights and observations of “in-the-wild” attacks, as well as in-depth and frequent conversations with the top cybersecurity researchers and CISOs worldwide, serve as the foundation for its research and product-related work.

4 Tips to Improve Cybersecurity for Your Business

Businesses of all sizes must be concerned about cybersecurity in today's interconnected world. Trust and survival depend on your company's ability to keep private information secret, protect consumer data, and repel cyberattacks. To better protect your company online, we've compiled five tried-and-true strategies.

KeePass CVE-2023-32784: Detection of Processes Memory Dump

During May, a new vulnerability CVE-2023-32784 was discovered that affected KeePass. KeePass is a popular open source password manager which runs on Windows, Mac, or Linux. The vulnerability allows the extraction of the master key in cleartext from the memory of the process that was running. The master key will allow an attacker to access all the stored credentials. We strongly recommend updating to KeePass 2.54 to fix the vulnerability.

CVE-2023-27997: Critical Fortinet Fortigate SSL-VPN RCE Vulnerability

On June 9th 2023, security researchers from Olympe CyberDefense published a blog stating that they responsibly disclosed a critical vulnerability in SSL-VPN firewalls to Fortinet. This vulnerability, CVE-2023-27997, is a critical, pre-authentication RCE vulnerability that impacts all versions of Fortinet SSL-VPN firewalls, even if multi-factor authentication (MFA) is enabled. The security researchers responsibly disclosed the vulnerability to Fortinet.

Snyk named a Leader, placed highest in Strategy category in The Forrester Wave: Software Composition Analysis (SCA), Q2 2023 report

We’re thrilled to announce that Snyk was named a Leader in The Forrester Wave™: Software Composition Analysis (SCA), Q2 2023 report! We believe this recognition — and the fact that we are ranked highest in the Strategy category out of all evaluated vendors — highlights the work we’ve done at Snyk to disrupt the industry with developer-centric application security solutions to help companies secure their software supply chain.

Mass Exploitation of MOVEit Transfer Critical Vulnerability - Recommended Mitigations and How Forescout Can Help

On May 31, Forescout Research – Vedere Labs uncovered a significant incident where threat actors exploited a critical zero-day vulnerability in the MOVEit Transfer software, which resulted in unauthorized access to and exfiltration of private data, as well as privilege escalation. MOVEit Transfer is a widely adopted managed file transfer (MFT) solution that enables organizations to securely exchange files with their business partners and customers.