Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Cloud Threats Memo: What We Can Learn From the Top 15 Routinely Exploited Threats of 2021

Have you ever wondered what vulnerabilities are exploited the most by threat actors? The answers you have been eagerly waiting for could be found inside a joint Cybersecurity Advisory (CSA) coauthored by the cybersecurity authorities of the United States (CISA), Australia (ACSC), Canada (CCCS), New Zealand (NZ NCSC), and the United Kingdom (NCSC-UK), plus the U.S. National Security Agency (NSA) and Federal Bureau of Investigation (FBI).
These aren't the npm packages you're looking for

Over the years, as a developer, I’ve built and deployed many applications through digital agencies, side projects, startups, and freelance work. With time-sensitive deadlines, client expectations, and delivery dates to consider, security wasn’t usually top of mind when npm installing an open source package. This often led to reworking and cleanup on deployments that had let in known vulnerabilities, adding to compounding timelines and client disappointment.

CIS Control 7: Continuous Vulnerability Management

The Center for Internet Security (CIS) provides Critical Security Controls to help organizations improve cybersecurity. Control 7 addresses continuous vulnerability management (this topic was previously covered under CIS Control 3). Continuous vulnerability management is the process of identifying, prioritizing, documenting and remediating weak points in an IT environment.

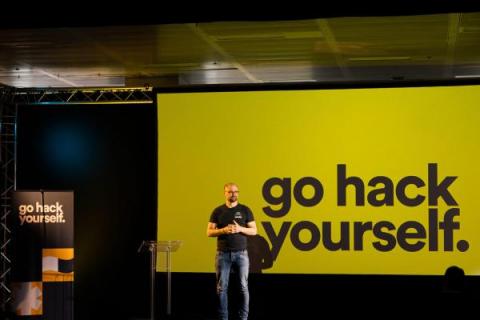
Phishing, OWASP, EASM, and hacking WordPress - top themes from Hack Yourself London

When Algolia’s security program manager Regina Bluman ran a Twitter poll to see how many people within the security industry understood the concept of EASM, she didn’t expect that the term is far from being on an IT security team’s radar. Moreover, most were not even aware of it.

CVE-2022-23648: Kubernetes Container Escape Using Containerd CRI Plugin and Mitigation

CVE-2022-23648, reported by Google’s Project Zero in November 2021, is a Kubernetes runtime vulnerability found in Containerd, a popular Kubernetes runtime. It lies in Containerd’s CRI plugin that handles OCI image specs containing “Volumes.” The attacker can add Volume containing path traversal to the image and use it to copy arbitrary files from the host to container mounted path. The vulnerability was reported by Felix Wilhelm on Nov.

Ignoring vulnerabilities with Snyk

Ignore a vulnerability? That sounds like a paradox. Why would anyone want to ignore a vulnerability? While ignoring security issues should not be your default practice, it is still sometimes necessary. Development and security teams today face vulnerability backlogs consisting of thousands of issues. To maintain rapid development, they must be able to effectively prioritize their work.

Vulnerability, Threats, Exploits and their relationship with risk

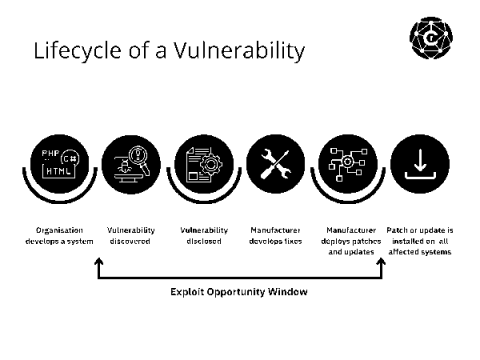
When protecting an organisation against cyber attacks, the words security threats, vulnerabilities, risk exposure, and sometimes exploits are seen very commonly. Unfortunately, these terms are not used correctly or interchangeably and are often left undefined.

Log4Shell, Splunkbase, and You: A Message From Your Friendly Neighborhood Cybersecurity Engineer

Call me David. As you might have heard, Log4Shell, “the single biggest, most critical vulnerability ever”1 was recently disclosed to the public. You may even have seen us make mention of it here, here, here, or even maybe here. Splunkbase was impacted by way of apps both made by Splunk and third-party developers.