Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How MSPs should evaluate AI security

AI is already incorporated into most of your clients’ workflows. Employees are using chatbots and other built-in GenAI tools to draft emails, analyze data and automate work. The challenge? Much of that activity is happening outside your formal security controls, and that creates a new risk layer. For managed service providers (MSPs), the question is no longer whether to secure AI adoption for their clients, but how to evaluate the right AI security solution.
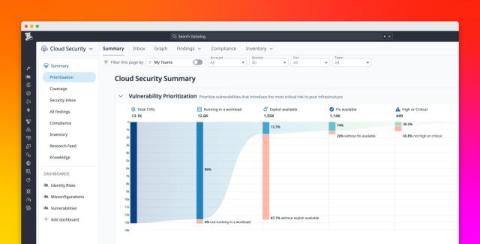
Securing the AI era: Outpace AI-powered attacks with unified security and observability

Security teams are dealing with a fundamentally different operating environment than they were a few years ago. AI-assisted development is rapidly pushing more code and infrastructure into production, and according to Datadog’s 2026 State of DevSecOps report, 40% of running services have an exploitable vulnerability.

Why Claude Mythos Changes AppSec Research, Not Your Scanning Stack

If you’re like our team, the morning after the Claude Mythos announcement brought more questions than answers. Among them: “Serious question. Do customers still need SAST?” It’s a fair question if you stop at the headline. Claude Mythos, Anthropic’s frontier AI model currently gated to vetted partners through Project Glasswing, had autonomously identified thousands of zero-day vulnerabilities across major operating systems and browsers . No rule books, no checklists.

Why the Biggest Breaches Still Come Down to the Basics | Nicole Perlroth at Black Hat

At Black Hat last year, Garrett Hamilton asked Nicole Perlroth what she wanted the next five years of security to look like. She didn't give the optimistic answer. She said she was genuinely terrified. Zero-day exploitation at scale, fully automated. Attackers turning AI into infrastructure of their own. A year isn't five. But it's enough to check the tape.

Securing the Agentic Enterprise with Behavioral Analytics and AI Visibility

By mid-2026, the question is no longer whether AI belongs in the enterprise. It’s already embedded in daily work, supporting research, development, customer engagement, and operations. AI agents now act on behalf of employees, automate decisions, and interact directly with enterprise data and systems. This shift creates a new security challenge.

Agentic AI is Calling Your APIs: Why Autonomous Agents are the New Attack Surface

On April 27, 2026, a threshold was crossed that the internet had never hit before. Cloudflare Radar data confirmed that automated systems, such as bots, crawlers, and autonomous AI agents, now generate 57.4% of all HTTP requests for web content. Human traffic accounts for just 42.6%. What is accelerating this transformation is agentic AI: autonomous systems that browse, search, authenticate, and transact on behalf of users without any human intervention mid-task.

How Shadow AI is Creating an Unmanaged Identity Crisis

Employees are adopting AI tools, agents and automations faster than organizations can govern them. The real danger emerges when these tools connect directly to internal systems and sensitive data in the name of enhancing productivity. Among employees who use AI at work, a significant share do so without formal approval from IT or security teams, which is commonly called shadow AI.

The massive AI collapse nobody is talking about #aisecurity #business #trending

Many AI companies are still running at a loss while businesses rush to build critical services on top of them. If compute costs rise and margins collapse, some of those vendors may disappear without warning, taking business critical processes down with them.

How AI Is Changing Both Cyberattacks and Cyber Defense

Artificial intelligence is changing cybersecurity because it gives both attackers and defenders more speed, scale, and flexibility. Attackers can use AI to write better messages, test code, scan targets, and move through stolen data faster. Security teams can use similar technology to detect odd behavior, sort alerts, and respond before a small incident becomes a serious breach. The biggest shift is not that AI replaces every hacker or every analyst. Work that once required hours, special training, or a larger team can now be assisted by software.
Featured Post

The Control Paradox: Why Regulated Industries Must Rethink AI in Security Operations

For decades, highly regulated sectors have taken a cautious approach to cybersecurity, and for organisations in industries such as banking and finance, healthcare, insurance and critical national infrastructure, the instinct has been to retain ownership of security operations. That model is now under strain. Escalating cyber threats, regulatory scrutiny, and a growing skills shortage are exposing the limits of traditional Security Operations Centres (SOCs). At the same time, AI-driven technologies are maturing rapidly and forcing a strategic rethink.